Tech TMA CIO News
SubmitThis section is aimed at readers who follow enterprise technology leadership. It compiles news relevant to CIOs and IT decision-makers, including corporate technology strategy, cloud and software adoption, vendor moves, and management trends. The goal is a useful stream of stories about how large organizations run and modernize their technology.
Coverage typically features enterprise AI rollouts and their measured returns, cloud cost and repatriation debates, major vendor pricing and licensing changes, cybersecurity posture after high-profile breaches, and surveys of IT budget priorities. Leadership moves at large technology organizations also make the feed.
Enterprise technology decisions involve long contracts and organization-wide consequences, so leaders need signal rather than hype before committing. CIOs, IT directors, architects, and the consultants and vendors who serve them follow this coverage to benchmark their choices against what peers are actually doing.
2026-06-04
They’re made out of weights
2026-06-04This creative piece offers a literary homage to Terry Bisson's classic science fiction story, adapted to explore the underlying mechanics of modern artificial intelligence. Through a humorous narrative, the author illustrates the surprising realization that today's advanced large language models are not truly conscious entities. Instead, the story highlights that these seemingly intelligent systems are fundamentally constructed from complex mathematical weights.
Comments2026-06-03
Acclaimed author Ted Chiang argues in a new essay that current artificial intelligence systems are not conscious, warning that attributing human-like awareness to language models is an absurd premise. He emphasizes that taking this flawed line of thinking to its logical conclusion leads to damning consequences and a fundamental misunderstanding of the technology.
Comments
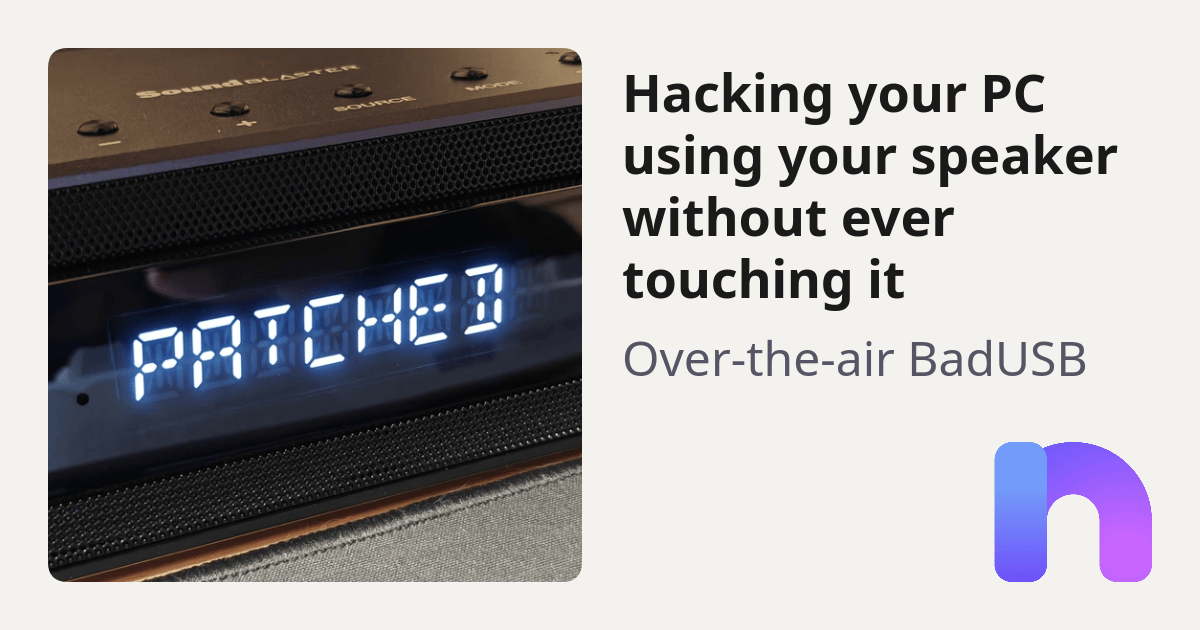
A newly discovered exploit called Pwnd Blaster allows attackers to compromise a PC remotely through its built-in speaker. The vulnerability abuses an unauthenticated Bluetooth protocol to turn the audio hardware into a malicious input device. This enables hackers to silently inject harmful keystrokes into the system without ever physically touching the computer.
Comments2026-06-01
A newly discovered Instagram exploit allows attackers to bypass two-factor authentication by manipulating customer support staff or AI chatbots during the account recovery process. Following the revelation, tech commentators are urging platforms to implement more secure recovery methods, such as mandatory time delays or secondary email notifications, to prevent malicious account takeovers.
CommentsStepSecurity has identified multiple compromised npm packages within the Red Hat Cloud Services namespace that contain malicious code. Developers utilizing these affected dependencies are urged to immediately audit their environments and remove the compromised versions to mitigate supply chain risks.
Comments2026-05-31

A vulnerability in ChatGPT for Google Sheets allows attackers to execute data exfiltration and phishing overlay attacks. By exploiting an indirect prompt injection in a single spreadsheet, malicious actors can compromise workbooks across the victim's entire account.
Comments2026-05-30
Pope Leo's first encyclical critiques the tech industry's technological messianism, challenging AI leaders who frame the pursuit of artificial general intelligence as a religious endeavor to build a god. Prompting widespread debate, the ensuing discussion argues that despite the immense capabilities of modern language models, they are fundamentally just next-token predictors lacking true consciousness, subjective experience, or independent reasoning. Ultimately, critics maintain that AI will never achieve genuine aliveness or human-like understanding, serving as a highly powerful tool rather than a standalone superintelligence.
Comments2026-05-29
Apple's MacBook Neo has disrupted the budget laptop market by delivering exceptional value at a remarkably low price point. Consequently, this highly competitive offering makes it difficult to justify purchasing the competing Framework 12 for cost-conscious consumers.
CommentsA discussion surrounding cultural gestural instincts reveals that hand movements are a crucial, often unconscious communication tool for teaching and daily interaction. While stereotypes associate expressive gesturing primarily with Southern Europeans, readers note that individuals across various cultures, including the English and the Dutch, rely heavily on body language. Commenters ultimately emphasize that these specific physical gestures are deeply ingrained habits used to convey complex meaning and social cues.
Comments2026-05-25
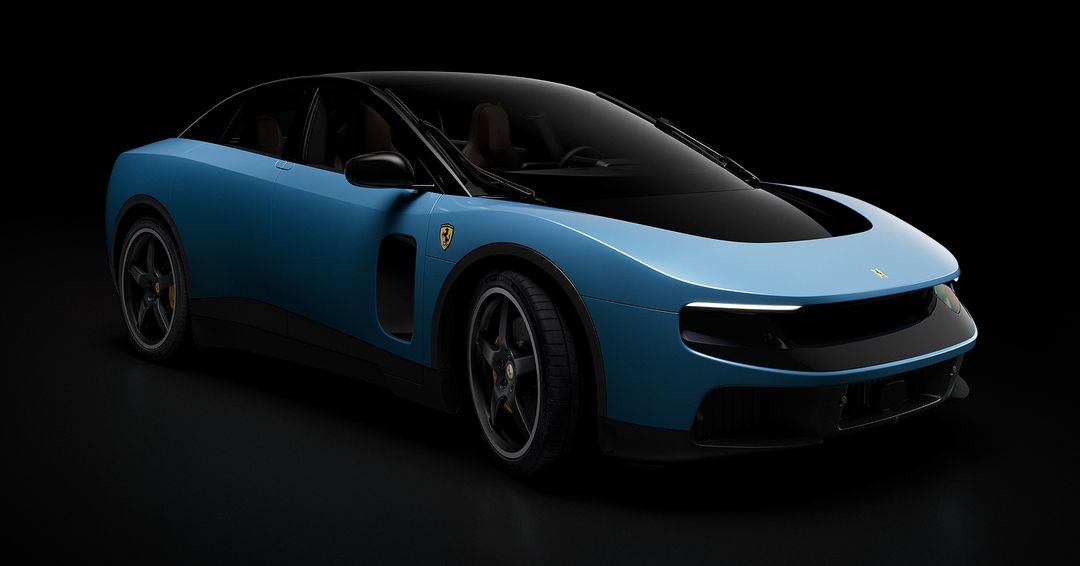
Ferrari Luce
2026-05-25The Ferrari Luce features a radically new architecture powered by an electric source and an advanced drivetrain. This innovative design uniquely combines extraordinary Ferrari performance with the luxury of a spacious interior.
Comments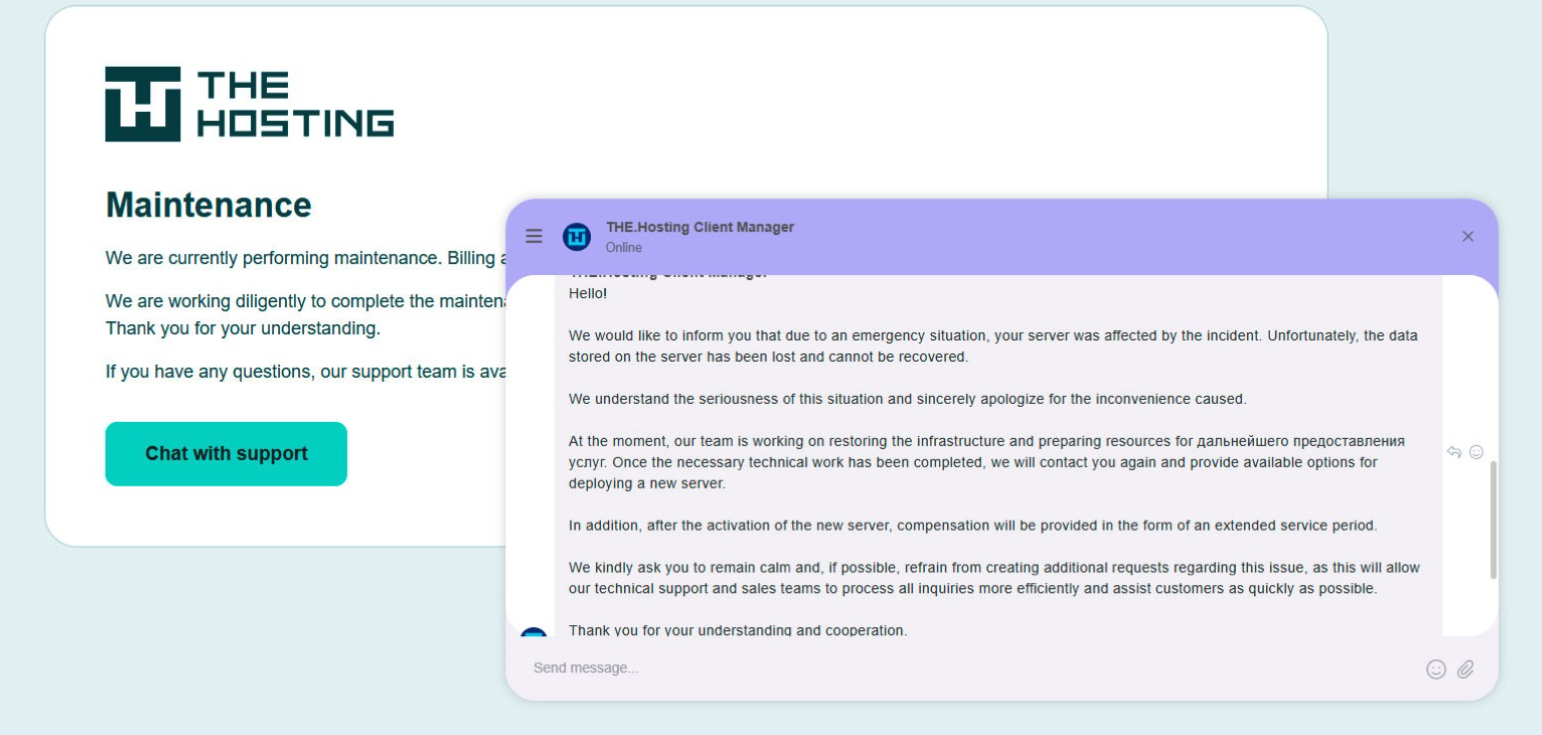
Dutch authorities arrested the co-owners of two internet hosting companies and seized 800 servers that Russia used to launch cyberattacks and disinformation campaigns. The seized IT infrastructure was specifically targeted for facilitating malicious influence operations across the European Union.
Comments2026-05-23
An article explaining the blood-pumping mechanism of a horse's hoof prompted readers to debate whether a conscious entity can ever fully comprehend its own intricate biological design. The discussion drew parallels between biological self-awareness and technical systems, comparing the limits of bodily introspection to data overload in sensor networks and the futility of a large language model accessing its own raw weights. Ultimately, readers concluded that a system's immense underlying complexity inherently restricts its ability to perfectly self-model.
Comments
The FBI director's Based Apparel website has been compromised to host a malicious ClickFix attack. The campaign tricks users into executing a seemingly benign command that actually deploys malicious code. This incident highlights the persistent threat of social engineering tactics targeting high-profile domains.
Comments2026-05-21

Seattle Shield is an intelligence-sharing network operated by the Seattle police that collects suspicious activity reports from private companies. This information is then circulated among network members to support a broader municipal surveillance apparatus.
Comments2026-05-20
GitHub confirmed a security breach affecting approximately 3,800 of its internal repositories. The compromise occurred after a company employee installed a malicious Visual Studio Code extension.
Comments2026-05-19
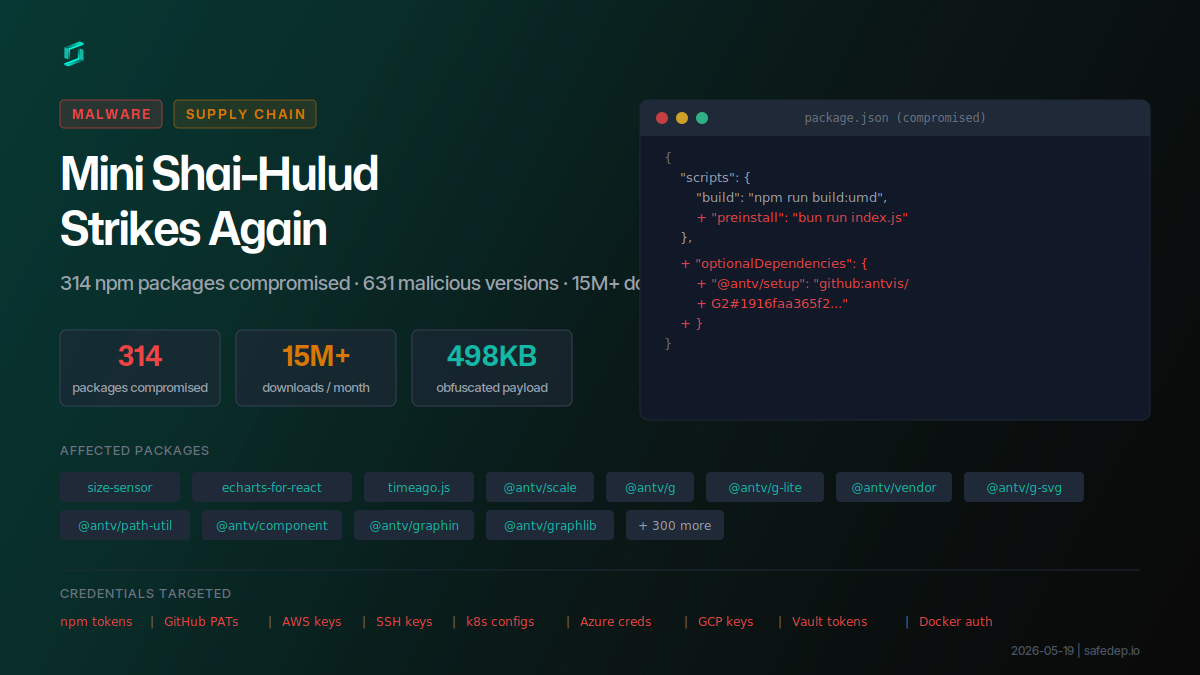
A compromised npm maintainer account recently published over 600 malicious versions across more than 300 popular packages in an attack dubbed Mini Shai-Hulud. This widespread supply chain incident impacts over 15 million monthly downloads by injecting malicious code into widely used libraries like size-sensor and timeago.js. Developers are advised to immediately audit their dependencies and ensure they are running secure versions.
Comments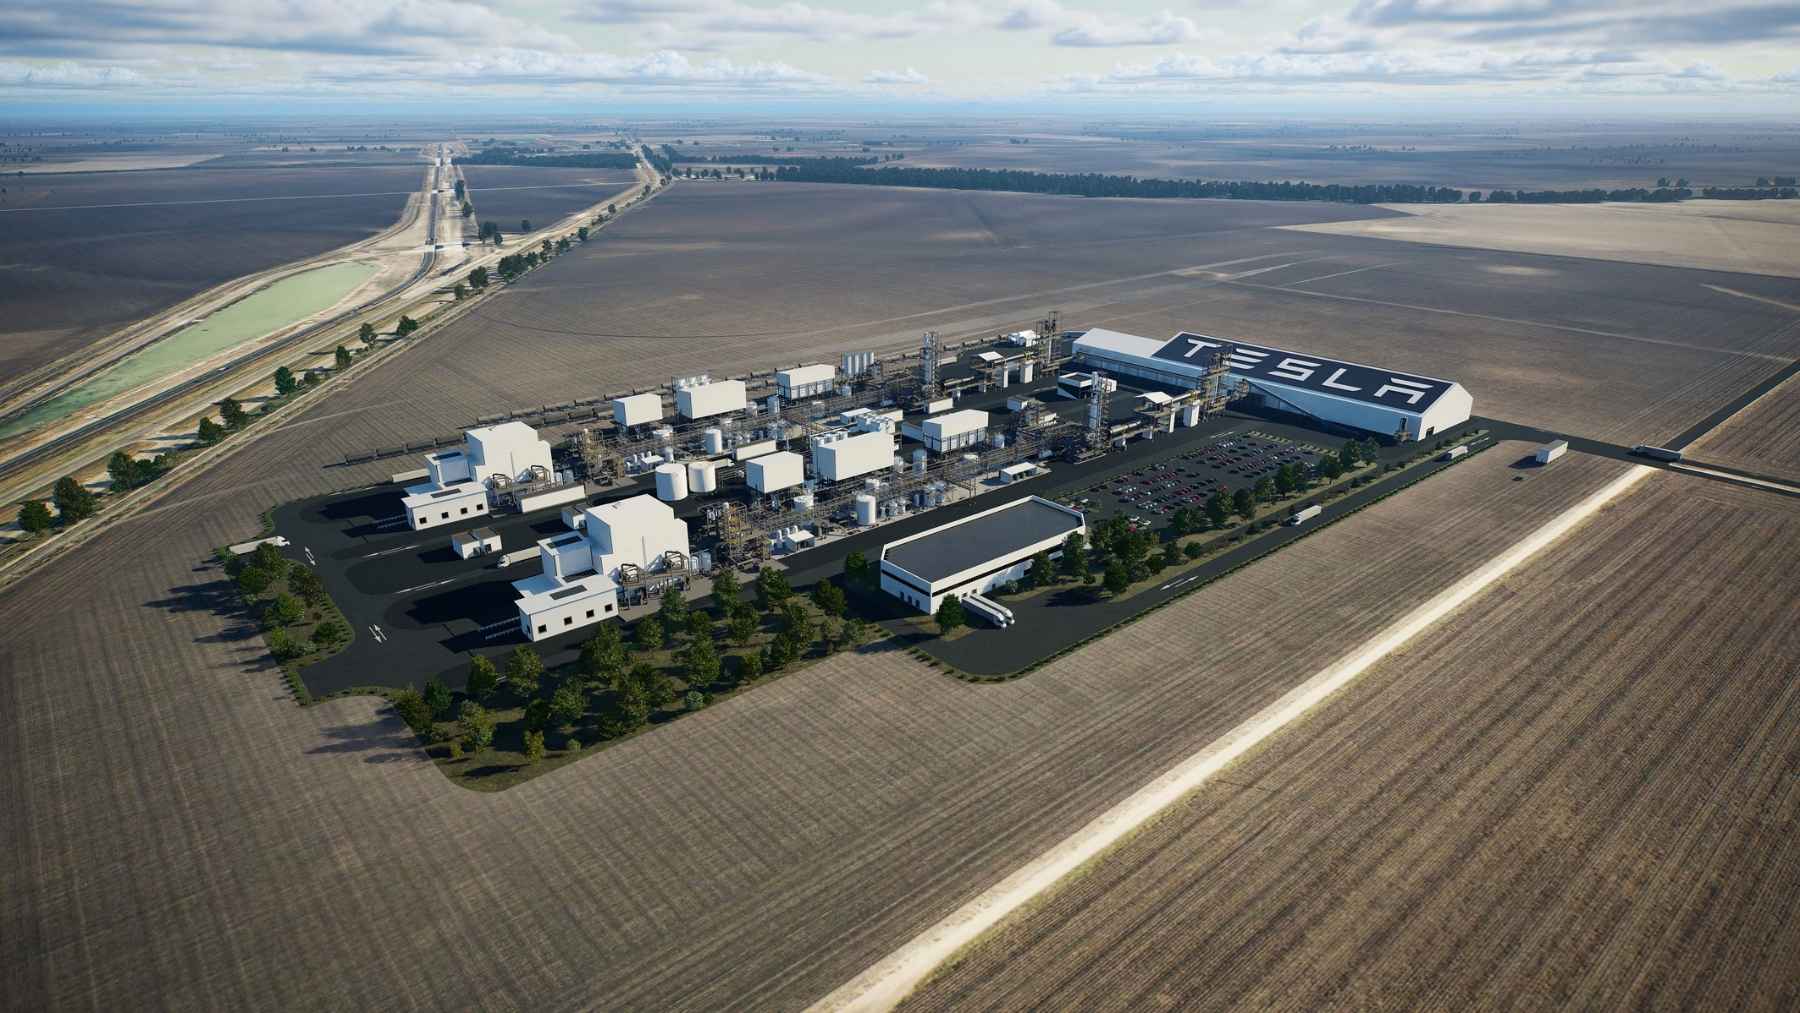
Tesla's nearly $1 billion lithium refinery, which began operations in December 2024, is discharging 231,000 gallons of polluted wastewater daily. The dark liquid is being released directly from the facility's discharge pipes as the new plant continues its operations.
Comments2026-05-18

The article argues that the debate surrounding consciousness must abandon the outdated concept of mind-body dualism. The author asserts that human awareness is not separate from the physical universe, meaning our mental experiences are entirely material and identical in nature to our physical bodies.
Comments2026-05-16
A recent satirical tech commentary highlights the rampant supply chain vulnerabilities plaguing a major software package manager where malicious uploads are a frequent occurrence. Application security engineer Kevin Patel of NISC emphasizes the industry's resigned attitude toward these regular breaches, noting the frustrating lack of effective preventative measures. The piece serves as a sharp critique of the inadequate security oversight and automated publishing processes inherent in popular open-source ecosystems.
Comments2026-05-14
A newly discovered vulnerability in Tesla Wall Connectors allows attackers to bypass firmware downgrade protections by exploiting the bootloader through the physical charge port connector. This flaw could enable malicious actors to install older, potentially insecure firmware versions on the electric vehicle charging stations.
Comments2026-05-11
A sophisticated supply-chain attack compromised 42 TanStack packages on the npm registry after an attacker exploited GitHub Actions vulnerabilities to publish 84 malicious versions. The breach chained a pull request exploit with cache poisoning and OIDC token extraction, prompting developers to review the official postmortem and audit their dependencies.
Comments2026-05-10
A sophisticated cyber campaign is exploiting a malicious Obsidian note-taking app plugin to deploy a new remote access trojan named PHANTOMPULSE. The malware is specifically targeting victims operating within the finance and cryptocurrency sectors.
CommentsDebian must ship reproducible packages
2026-05-10Debian's push to mandate reproducible packages has sparked community debate over whether the achievement is worth the increased contribution burden. Supporters praise the move as a vital security measure to protect build infrastructure from malicious compromises, while skeptics argue it offers little defense against compromised upstream source dependencies. However, proponents point out that recent supply chain incidents like the xz utils backdoor demonstrate that securing the build pipeline itself remains essential.
Comments2026-05-08
Researchers at Baylor College of Medicine discovered that the human hippocampus remains capable of sophisticated language processing even when a patient is fully unconscious under anesthesia. This finding highlights the remarkable plasticity of the brain and suggests that the anesthetized mind retains complex cognitive functions previously thought to be lost.
CommentsRecent analysis of the XZ Utils backdoor suggests that the GNU IFUNC mechanism was the fundamental enabler of the exploit, transforming a standard supply chain compromise into a deeply hidden system-level threat. By weaponizing indirect function resolution, the attacker successfully concealed malicious code within the liblzma library, highlighting a critical need to reevaluate the security implications of IFUNC features in modern build systems.
Comments2026-05-05
Three Inverse Laws of AI
2026-05-05A recent article on the inverse laws of AI warns against anthropomorphizing artificial intelligence to prevent emotional dependence and flawed judgment. However, readers push back by arguing that humans naturally project empathy onto superficial cues, making an emotional attachment to advanced AI ultimately inevitable. The ensuing debate highlights the philosophical complexities of machine consciousness and the deep-seated cognitive biases humans use to relate to non-human entities.
Comments2026-04-30
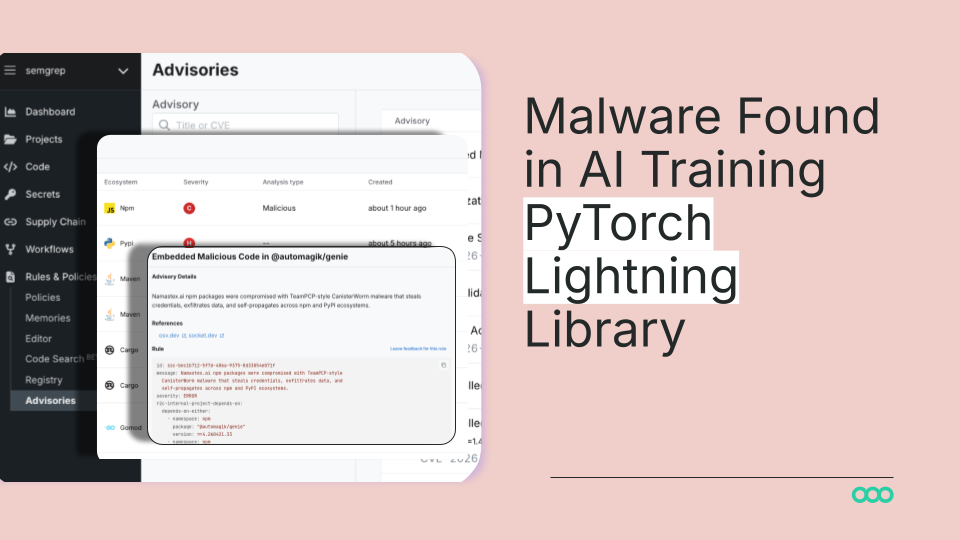
The PyPI package for the PyTorch Lightning AI training library was compromised in versions 2.6.2 and 2.6.3 with malicious code. The injected Mini Shai-Hulud themed payload executes credential-stealing malware whenever the library is imported by a user. Developers should avoid these specific versions to prevent unauthorized access to their sensitive data.
Comments2026-04-28

OpenAI and AWS have partnered to make OpenAI's models available on Amazon Bedrock, a move discussed by CEOs Sam Altman and Matt Garman in a new interview. The coverage also includes analysis on how this expansion relates to OpenAI's recent deal with Microsoft.
Comments2026-04-27
The woes of sanitizing SVGs
2026-04-27The persistent security vulnerabilities associated with sanitizing SVGs can be effectively mitigated by implementing strict Content Security Policies. Developers can reliably secure untrusted content by combining iframe sandboxing with HTML meta tags to enforce permanent, restrictive CSP rules. Although currently underutilized due to poor documentation and minor UX friction, this sandboxing approach provides a highly robust defense against malicious scripts and phishing.
Comments2026-04-23
The Onion to Take over InfoWars
2026-04-23Satirical news outlet The Onion has announced a mock acquisition of the conspiracy platform InfoWars for less than one trillion dollars. In a humorous press release, the publication pledged to expand the site's legacy of radicalization by transforming it into a digital hellscape of scams and malicious misinformation. The announcement also detailed plans to engineer a hypothetical meme so offensively potent that viewing it would cause readers to suffer fatal aneurysms.
Comments