news
213
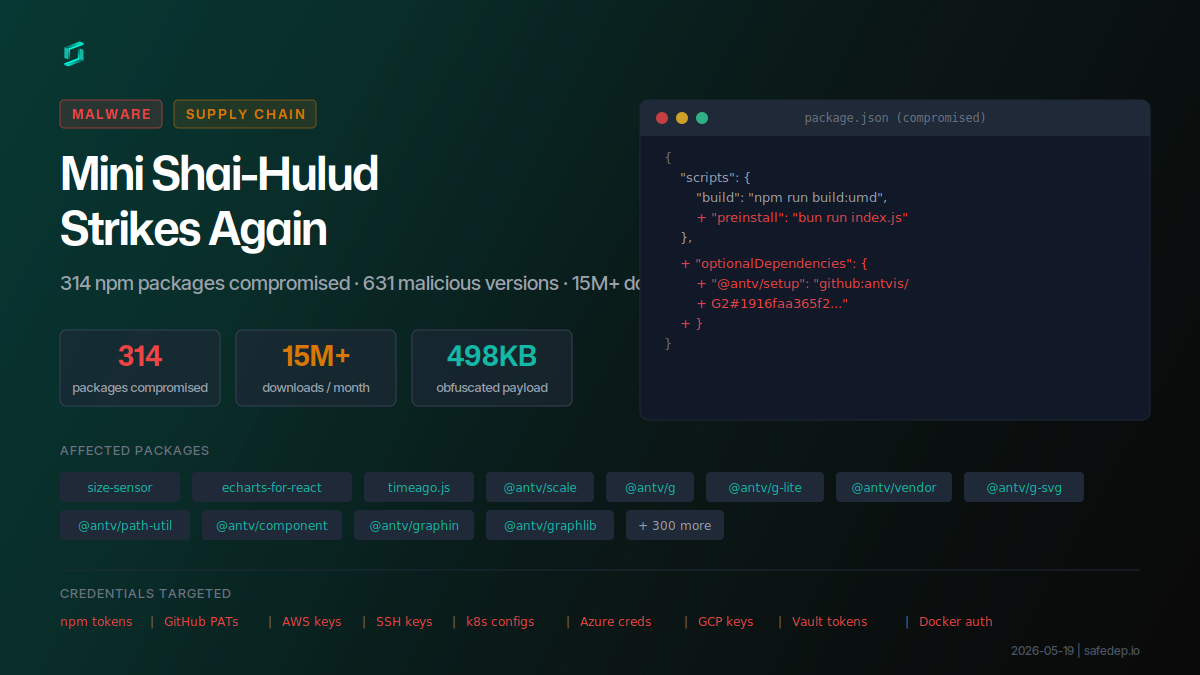
A compromised npm maintainer account recently published over 600 malicious versions across more than 300 popular packages in an attack dubbed Mini Shai-Hulud. This widespread supply chain incident impacts over 15 million monthly downloads by injecting malicious code into widely used libraries like size-sensor and timeago.js. Developers are advised to immediately audit their dependencies and ensure they are running secure versions.
Comments
0Discuss on Hacker NewsOnly full members can comment
Log in to express your opinion.
No comments yet.