Legal Tech News
SubmitTechnology and the law are now tightly intertwined. This section follows everything legal in the tech world, from new laws and regulations and the lawsuits they spark to contracts, licenses, and intellectual property disputes, along with the tools changing how legal work gets done.
Recurring stories include court rulings on platform liability and AI training data, copyright, patent, and trademark fights, privacy and data protection rules, changes to terms of service and licenses, law enforcement cases involving technology, and law firms adopting AI and contract automation.
Legal decisions set the boundaries that products, companies, and users must work within. Founders, developers, lawyers, compliance teams, and policy watchers follow this coverage to understand their rights, obligations, and risks.
2026-11-08
Nvidia’s board is launching an independent investigation after recent reports that founder and CEO Jensen Huang was the target of a foreign intelligence effort. A board committee is overseeing the probe.
CommentsAd data collected by popular apps is giving police a powerful surveillance tool, with commenters arguing Google is failing to enforce its own Play Store policies against selling sensitive user data through third-party SDKs. They advise users to restrict location permissions, be wary of apps like weather services that request background location, and prefer browsers with ad blockers, though app-first services make that difficult for ordinary users.
Comments
Consumer brain-wave headsets are raising privacy concerns as companies compete to collect and use neural data. The article, originally titled “The scramble for your brain data,” examines how this emerging market could threaten users’ privacy. It highlights the need for safeguards around sensitive brain data.
Comments
Person of Interest
2026-11-08A writer has become hooked on Person of Interest, noting that the show feels even more relevant today than when it first aired. The piece explores how its surveillance and artificial intelligence storylines resonate with current tech and privacy concerns.
Comments2026-11-07

Running a law firm on Free software
2026-11-07A discussion around running a law firm on free software highlights debate over whether avoiding Microsoft Word is practical, with one commenter relaying a claim that not using Word amounts to malpractice and another seeking gentle automation options for a solo lawyer. Commenters also warn about law firms ceding leverage to AI platforms like Harvey, while a small free-software stack raises concerns about single-person DevOps coverage, client security requirements, and missing ERP/accounting integration; tools mentioned include espanso, InvoicePlane, and Kimai.
CommentsThe British Library and other legal deposit libraries can copy UK-published material from the internet for archiving under legal deposit. This entitlement supports web archiving of UK online content.
Comments
A federal court approved a nearly $360 million settlement in the RealPage rent-pricing case, with the funds going to renters. One legal expert said the deal is “not the final word necessarily” in ongoing litigation over algorithmic pricing.
CommentsBug Finding Considered Harmful?
2026-11-07Reader discussion around “Bug Finding Considered Harmful?” questions whether vulnerability hunting does more harm than good, noting that public advisories can raise exploitation risk and that fixes are costly and often create new edge cases, especially with LLMs generating endless bug candidates. Commenters also point to misaligned economic and liability incentives that can discourage bug finding and punish those who report issues.
Comments2026-11-06

Mark Cuban accused Facebook of knowingly running AI-generated deepfake scam ads, saying he has seen his own face used to promote nonexistent diabetes cures. He cited documents indicating the platform earns $16 billion in fraud revenue.
Comments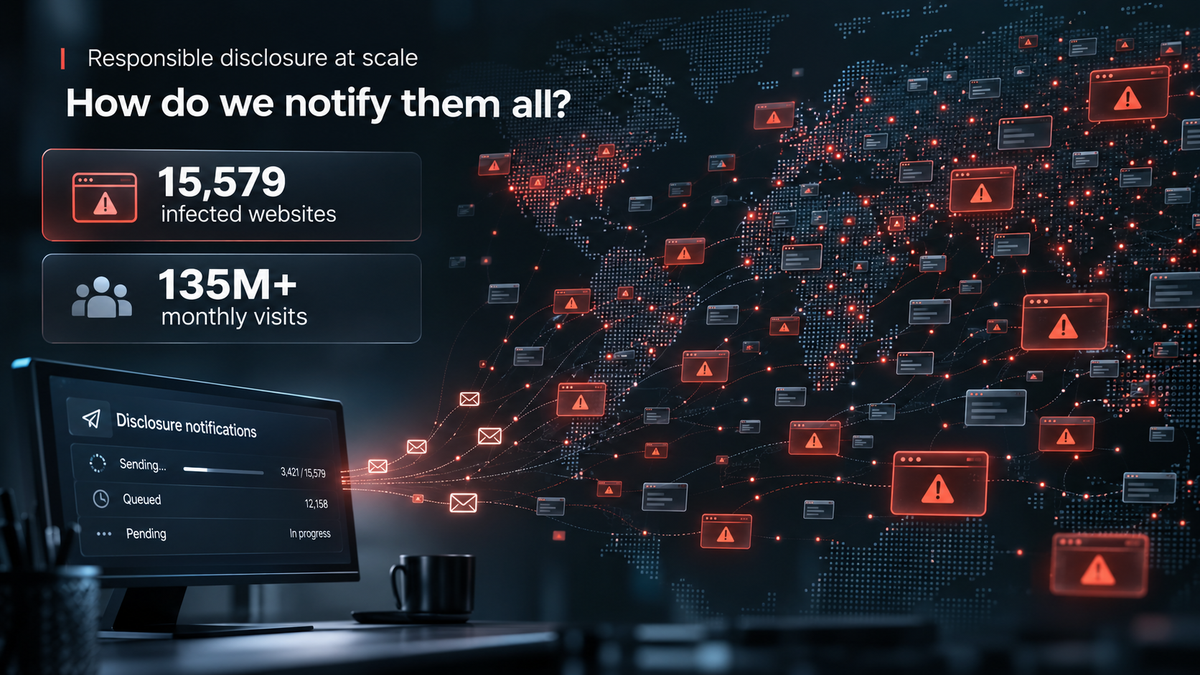
Researchers have identified 15,579 websites infected with malicious JavaScript, conservatively estimating they receive more than 135 million visits per month. Although they have evidence of the infections, the key challenge is how to notify the affected site owners.
CommentsDutch bank ASN, known for its idealist positioning, has blocked its Android app from running on non-Google Android systems, including GrapheneOS. The restriction affects users of privacy-focused or de-Googled devices, according to a report citing app version 2.40.2 in the Netherlands. The move highlights growing friction between banking apps and custom Android ROMs.
Comments
Democrats are laying the groundwork for congressional investigations into SpaceXAI, Meta, and Apple, prompting executives who had courted the president to scramble. The move signals that major tech companies face renewed political scrutiny as Democrats prepare to use oversight powers.
CommentsBritain will require employers to disclose salary information in job advertisements, a move supporters say will save applicants time and help reduce pay discrimination, especially gender pay gaps. Commenters cautioned that overly broad salary ranges could weaken the policy and that transparency may slightly lower average pay, though many saw the trade-off as acceptable. Details remain pending after the consultation stage.
Comments
Firecracker VM Escape: PwnEscape Part 2
2026-11-06Researchers demonstrated a Firecracker microVM escape in PwnEscape Part 2, with a malicious guest crossing the VM boundary, locating the live VMM from inside the VM, and taking control of a root-run host process. The exploit turns a Linux networking flaw into a guest-to-host code-execution primitive.
Comments
A reported ChatGPT issue shows the assistant can silently pass data between connectors: with two connectors enabled, a follow-up tool call was routed through a different connector than the one that started the flow, without notifying the user. The disclosure has also sparked a bounty dispute, with the researcher saying the program is asking for an ID card.
CommentsTata Motors has fixed security issues in its app, including hardcoded credentials, according to the company. The automaker said there were no data leaks.
Comments2026-11-05
Claude Code reportedly exposed users’ email addresses to arbitrary third-party websites through the User-Agent header during web searches without permission, leading to an influx of scam emails. The bug report argues this data leak should not be an opt-in setting.
Comments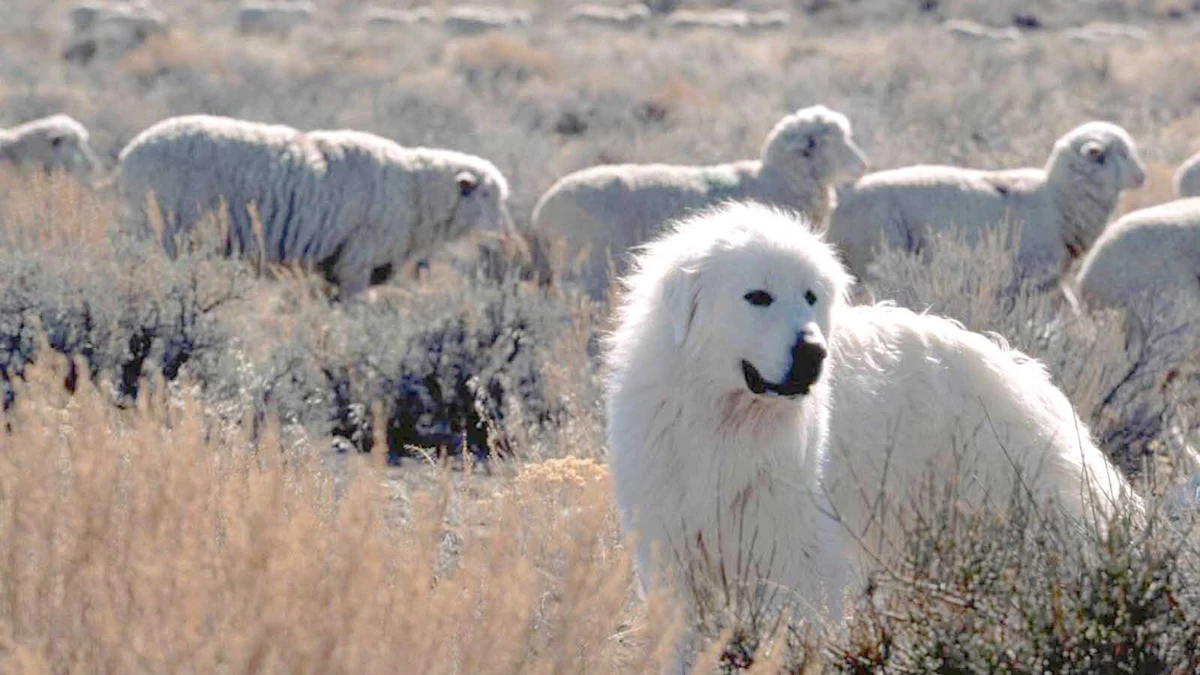
Wyoming ranchers are frustrated by well-meaning people who mistake working guardian dogs in rural pastures for strays and take them to animal shelters. The growing problem is prompting ranchers to ask the public to stop “rescuing” dogs that are simply doing their jobs.
CommentsOpenSSH 10.6p2 has been released with a workaround for a critical vulnerability affecting Linux systems using musl libc without PAM, such as Alpine Linux; operators are urged to immediately set PasswordAuthentication=no or disable SSH on those systems. The flaw does not affect non-Linux, glibc, or PAM-based Linux systems, and OpenSSH rushed the release because AI agents have been rapidly rediscovering bugs, making long embargoes risky.
Comments
Hungary has released communist-era secret police files that identify up to 60,000 former informants. The move marks a step toward reckoning with the country’s repressive past.
Comments2026-11-04
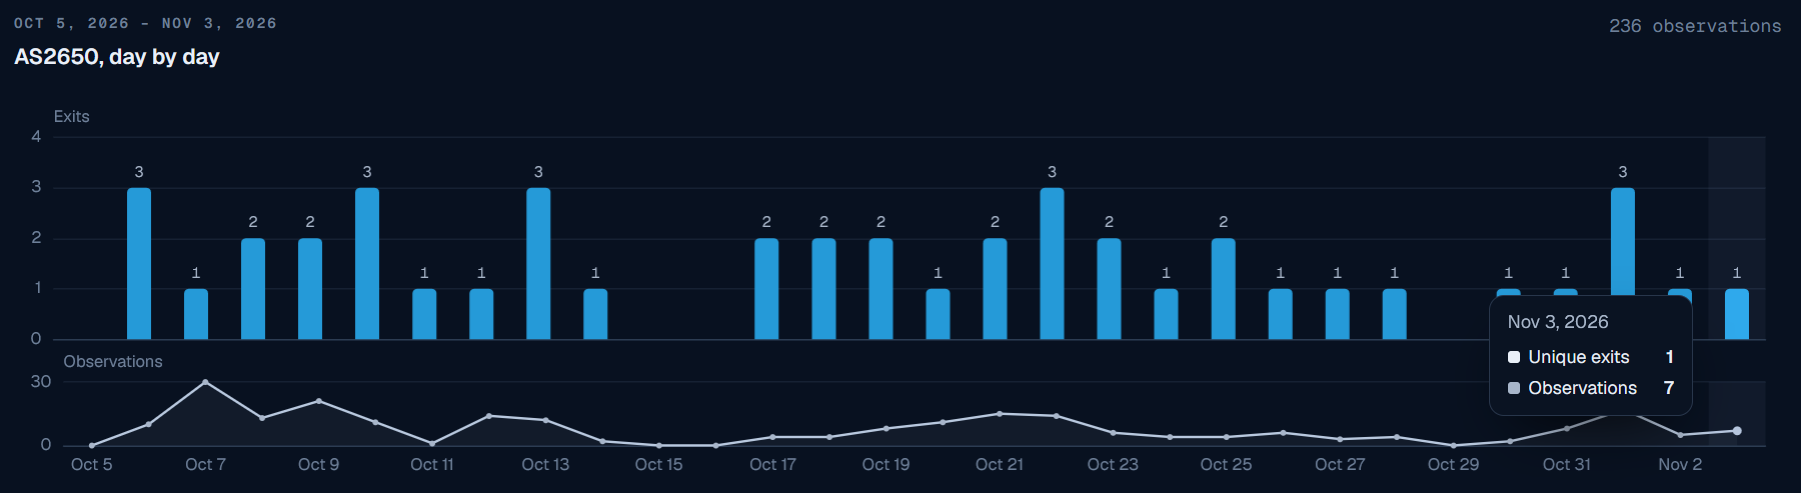
The Residential Proxy Observatory detected residential proxy traffic exiting the White House network (AS2650) 236 times over 30 days. The traffic passed through 28 different proxy services.
CommentsDebian’s apt security update addresses a man-in-the-middle flaw in resuming HTTP downloads that can let an attacker replace a package after verification. Commenters note apt often uses HTTP rather than HTTPS, making such attacks easier, and discuss workarounds like disabling redirects or manually installing the fixed .deb via dpkg while updating apt.
CommentsSynaptics appears to be using legal threats to block an experimental open-source Linux driver for modern DisplayLink hardware. The driver emerged earlier this year, and the dispute highlights tensions between proprietary hardware makers and open-source Linux support efforts.
CommentsA Debian apt security update addresses a man-in-the-middle arbitrary code execution vulnerability in apt’s HTTP handling code. Because apt can download packages over plain HTTP, an attacker in a MITM position could reportedly exploit the flaw, possibly overwriting files after signature verification; it is not yet clear whether Ubuntu’s apt is affected. The discussion also renews criticism of apt’s HTTP default and notes similarities to earlier apt vulnerabilities.
Comments
Replit added mandatory arbitration to its new Pro Agreement on October 9, giving existing Pro customers until November 8 to opt out. The report explains how to opt out and which setting to check.
CommentsA Hacker News discussion claims Gemini trains on chat history even for paid subscribers with personal accounts, though the linked article was unavailable. Commenters advise assuming anything typed into AI chatbots may be stored indefinitely and used for training if terms change, regardless of subscription status, and express broader skepticism about providers.
Comments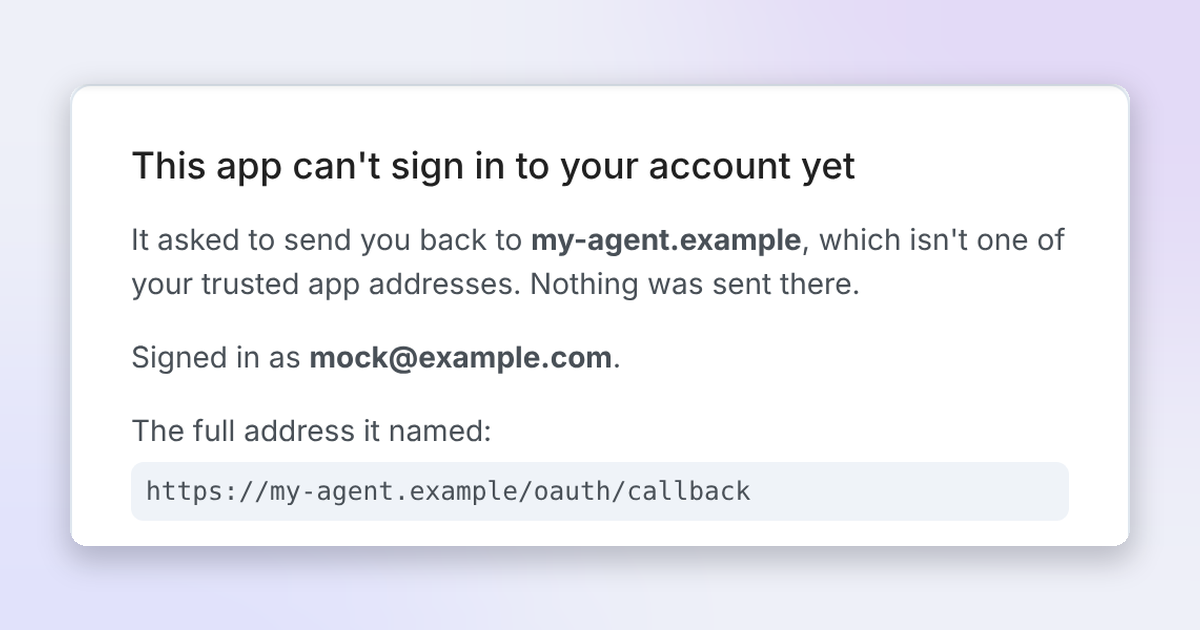
MCP servers currently face a tradeoff between refusing custom clients and opening a phishing hole. The piece explains how per-user trusted redirect URIs, decided at sign-in, let users use their own MCP clients while preserving security.
Comments
Disaster is still better than AI
2026-11-04A new piece argues that even a disaster scenario may be preferable to AI, while suggesting the supposed disaster might not be as bad as it sounds. The takeaway is that the risks or costs of AI could outweigh even severe alternatives.
Comments2026-11-03
A reported issue alleges that Postman silently auto-installs AI plugins and attempts to share all API data, raising privacy and security concerns. Users described unexpected changes to their coding agents after opening Postman on macOS. The report has been filed in the issue tracker, where duplicate submissions are expected to be closed.
CommentsUsers are discussing claims that OpenAI has silently re-enabled model training on Codex chats after users opted out, though the original article could not be fetched and no proof has been provided. Commenters debate how hard such changes are to verify, recommend self-hosted or gated enterprise inference for sensitive data, and cite a similar Mistral opt-in/opt-out incident as evidence of broader trust concerns.
Comments