Tech TMA CIO News
SubmitThis section is aimed at readers who follow enterprise technology leadership. It compiles news relevant to CIOs and IT decision-makers, including corporate technology strategy, cloud and software adoption, vendor moves, and management trends. The goal is a useful stream of stories about how large organizations run and modernize their technology.
Coverage typically features enterprise AI rollouts and their measured returns, cloud cost and repatriation debates, major vendor pricing and licensing changes, cybersecurity posture after high-profile breaches, and surveys of IT budget priorities. Leadership moves at large technology organizations also make the feed.
Enterprise technology decisions involve long contracts and organization-wide consequences, so leaders need signal rather than hype before committing. CIOs, IT directors, architects, and the consultants and vendors who serve them follow this coverage to benchmark their choices against what peers are actually doing.
2026-11-11

Flapping Airplanes raised $1 billion, partly by demonstrating a megakernel framework that performs efficient forward and backward passes while, oddly, playing Doom. Hyperstition’s Hyperkernel generates high-performance kernels for a range of models, as both efforts aim to make model execution faster.
Comments2026-11-10

Toyota is reviving its Scion brand with an unusual lineup for the American market. The relaunched Scion plans to sell a kei truck, a bike, and a hybrid side-by-side.
Comments
2026-11-09
Readers push back on the claim that no one will again build a Wikipedia-like project, citing OpenStreetMap, TV Tropes, fandom wikis and other volunteer crowdsourced efforts that continue and could evolve toward more semantic knowledge systems. They also warn that such projects face long-term strain from younger users’ reliance on corporate app stores, suspicion of libre/altruistic efforts, fewer obvious gaps for newcomers to fill, corporate free-riding and API abuse, and licensing barriers.
Comments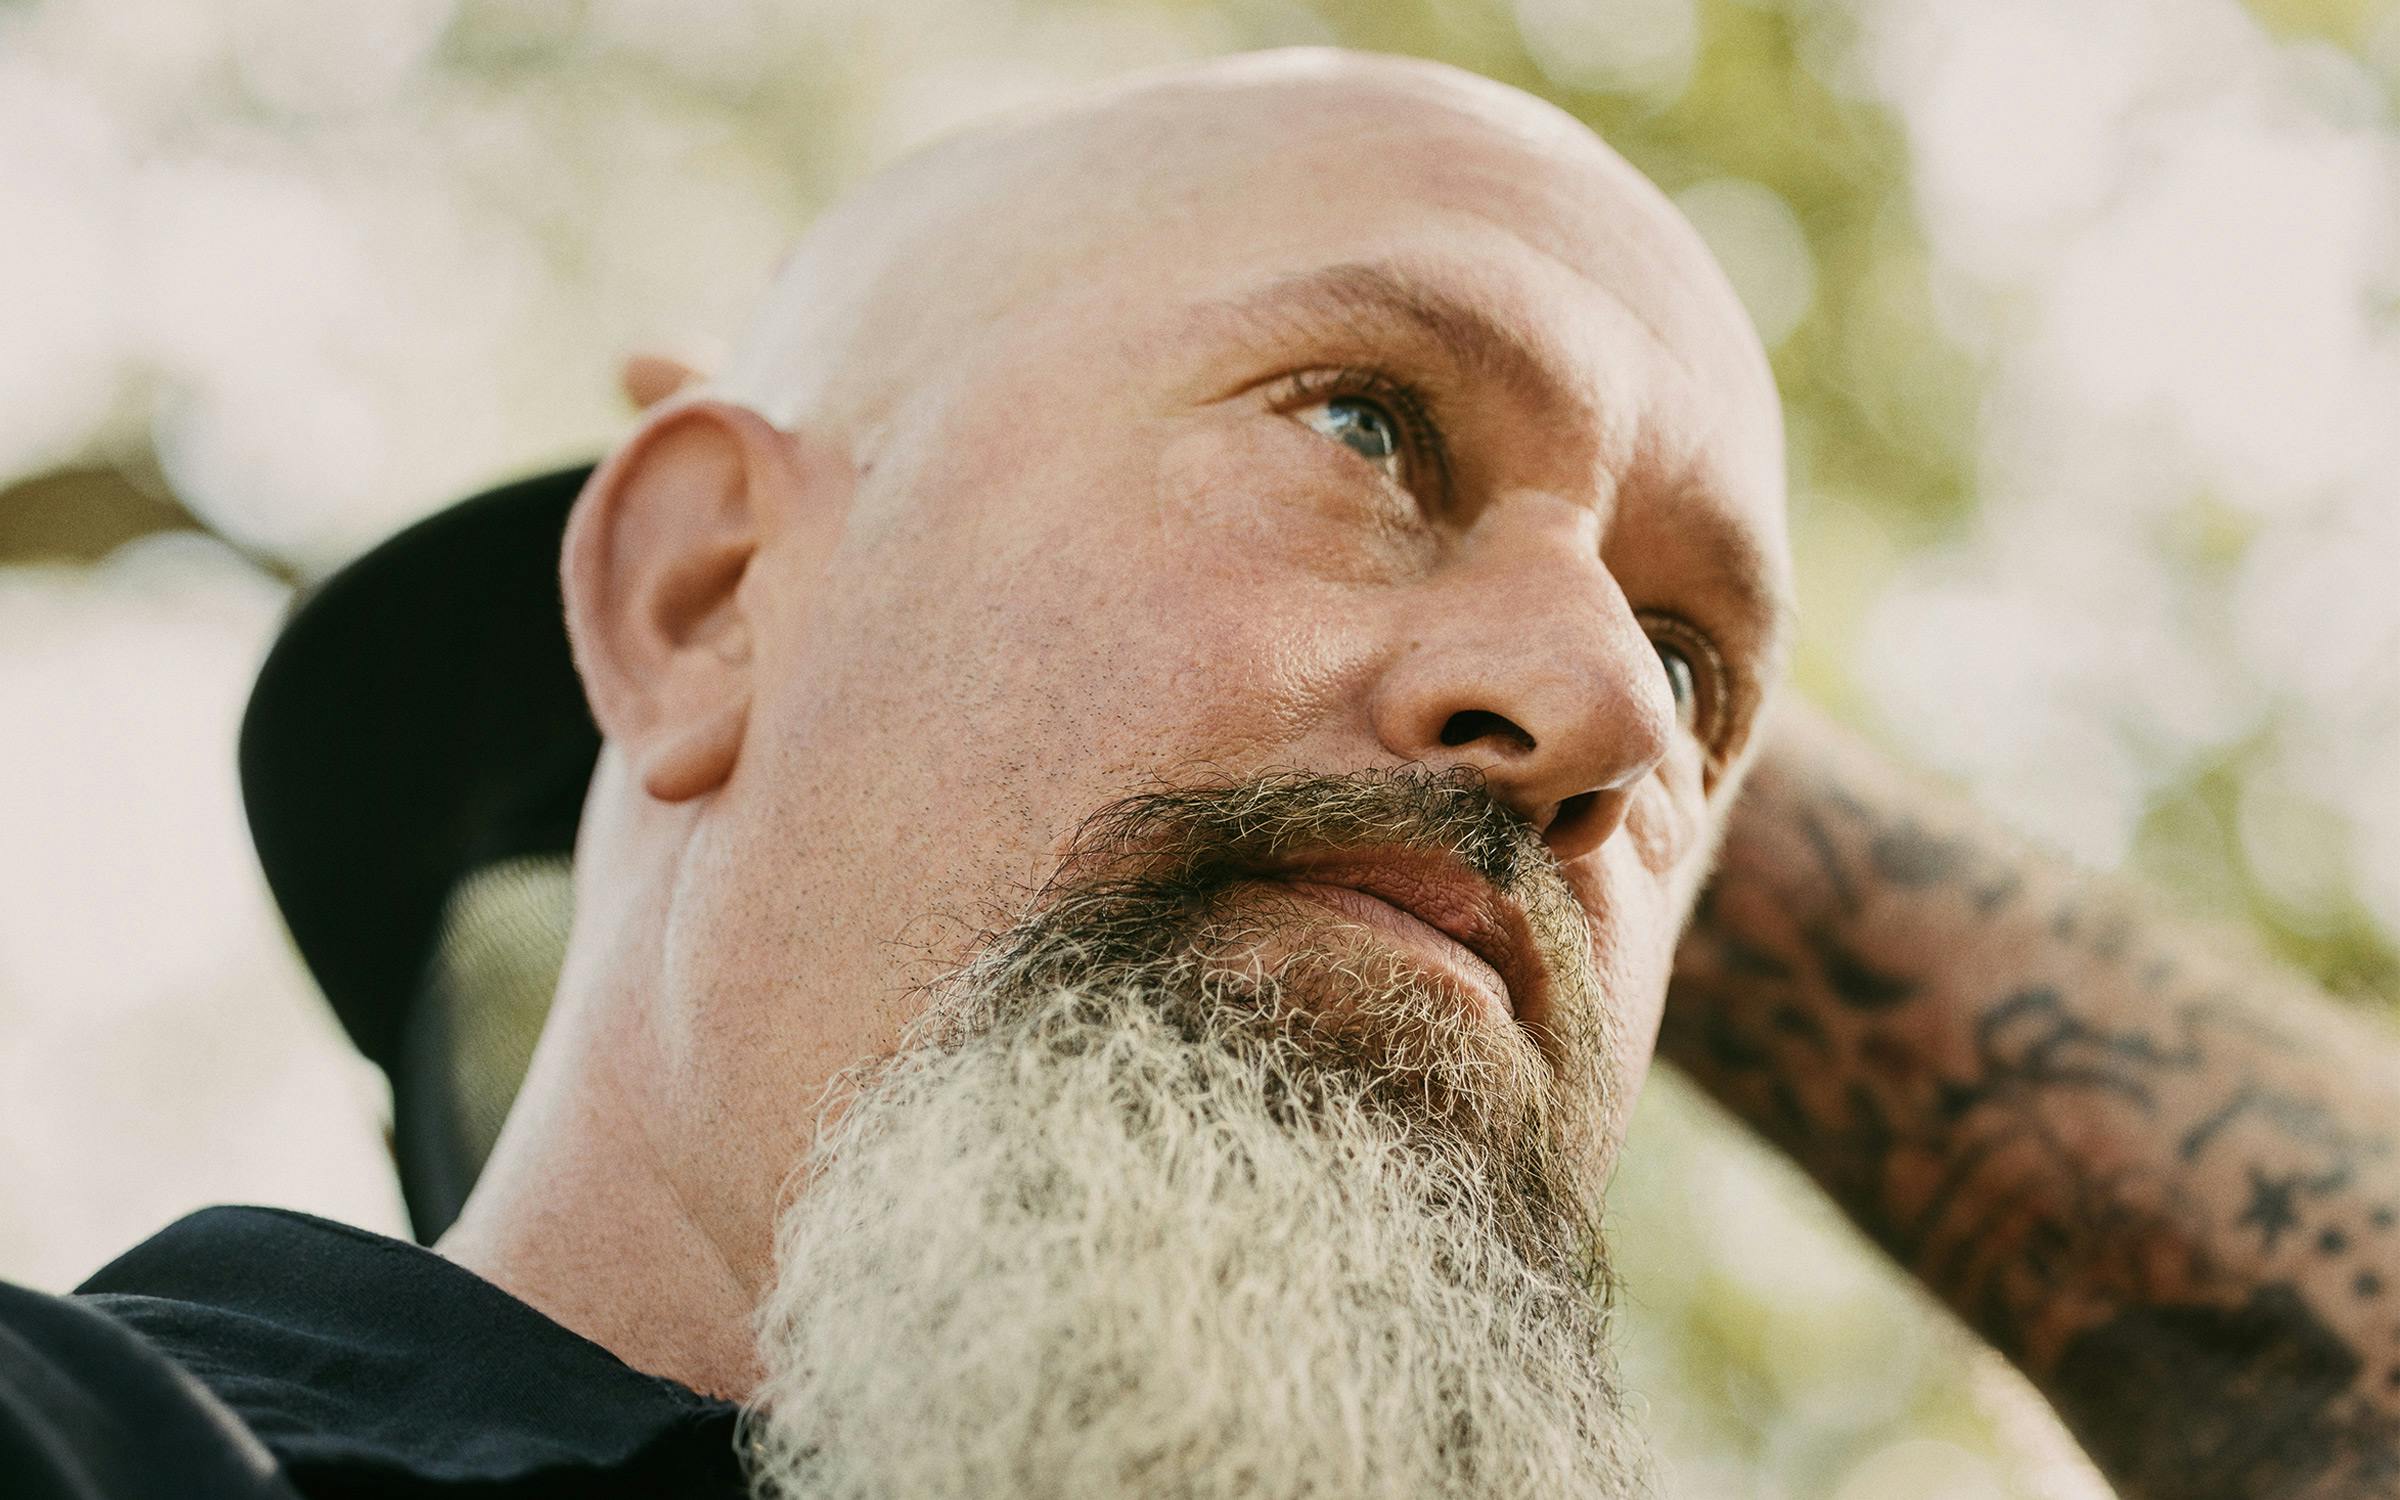
Forrest Welborn spent three decades as a suspect in the infamous Austin Yogurt Shop murders and was finally exonerated this year, yet he says he still doesn’t feel free. The article explores the lasting toll of living under suspicion and how exoneration has not erased the trauma.
Comments
The Kekulé Problem – Cormac McCarthy
2026-11-09In Cormac McCarthy’s essay “The Kekulé Problem,” he asks where language came from and argues that it likely arose from the unconscious mind rather than conscious invention, using Kekulé’s dream of the benzene ring as an analogy. McCarthy suggests language is a problem solved beneath conscious awareness, leaving its ultimate origins mysterious.
Comments2026-11-06
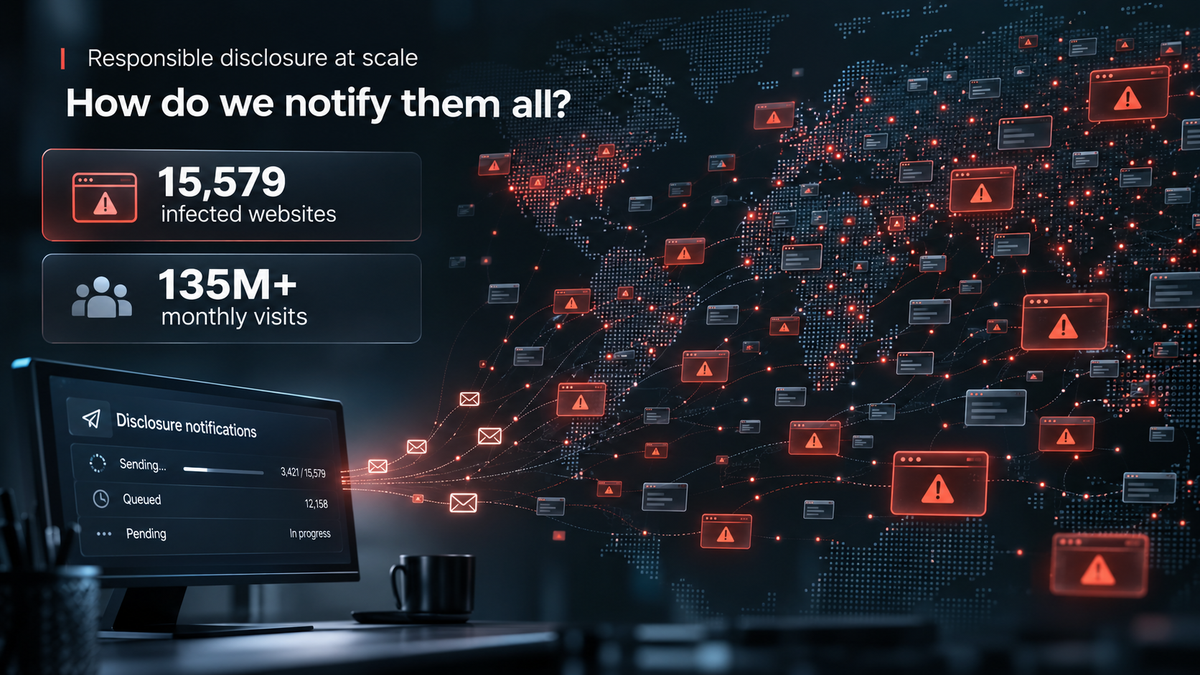
Researchers have identified 15,579 websites infected with malicious JavaScript, conservatively estimating they receive more than 135 million visits per month. Although they have evidence of the infections, the key challenge is how to notify the affected site owners.
Comments
Firecracker VM Escape: PwnEscape Part 2
2026-11-06Researchers demonstrated a Firecracker microVM escape in PwnEscape Part 2, with a malicious guest crossing the VM boundary, locating the live VMM from inside the VM, and taking control of a root-run host process. The exploit turns a Linux networking flaw into a guest-to-host code-execution primitive.
Comments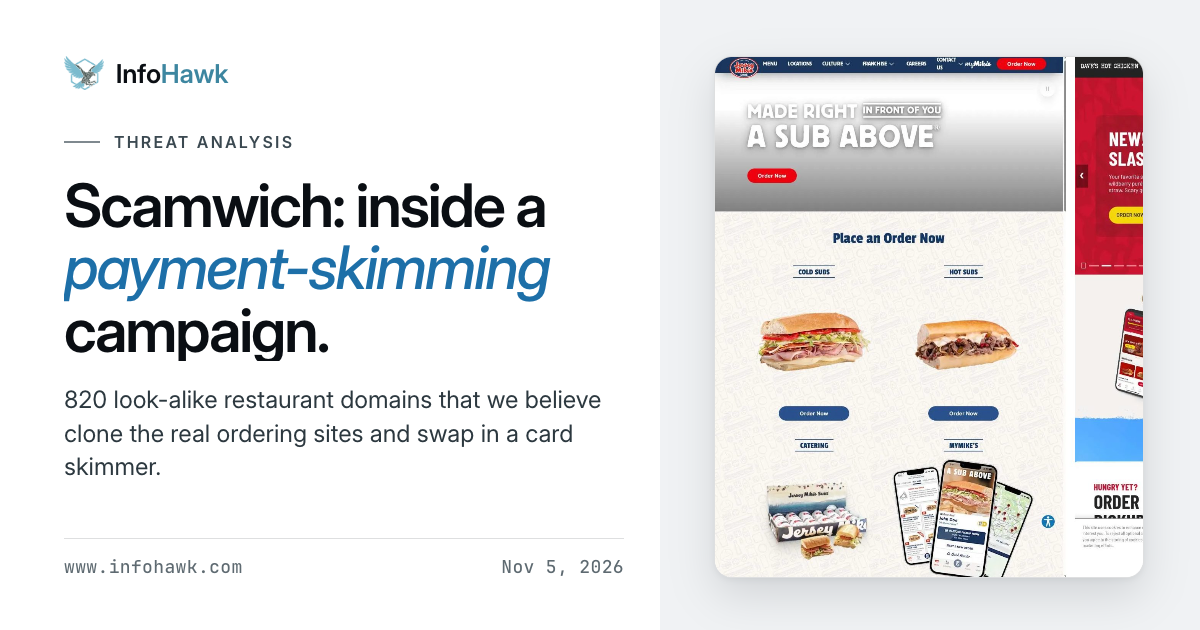
InfoHawk uncovered 820 suspicious restaurant domains impersonating major U.S. chains including Jersey Mike’s, Jimmy John’s, Firehouse Subs, Chipotle, and Dave’s Hot Chicken. Some of the sites run payment-skimming attacks that capture credit card data and ask customers for their bank’s SMS verification codes.
CommentsCloneGuard is a read-only, dependency-free tool that scans a repository for malicious tricks before you run it. It detects credential theft, hidden network calls, obfuscated code, and auto-run hooks.
Comments2026-11-05
A remote code execution vulnerability affects the modern Microsoft Paint app from version 11.0.0.0 up to but not including 11.2605.91.0, with users reporting the fix is available through the Microsoft Store rather than Windows Update. Microsoft's advisory describes it as network-exploitable without authentication or user interaction, while discussion also raised concerns about malicious BMP files.
Comments2026-10-31

We Took over ChatGPT Accounts
2026-10-31Researchers claim they could take over any ChatGPT account by sending a malicious link that bypassed the platform’s sandbox and content security policy. The finding highlights serious account-security risks in AI chatbot integrations.
Comments2026-10-30
The piece argues that dismantling the open web will not stop malicious bots, and that policymakers should not treat anonymity as inherently wrong. It urges targeted action against bad actors rather than broad restrictions on anonymity and open internet principles.
Comments
Embraer’s Atech aims to double in size by 2030, betting on drone traffic control and other civil-market technologies. The company is developing solutions to support safe coexistence in airspace, CEO Rodrigo Persico told Bloomberg Línea.
Comments2026-10-29
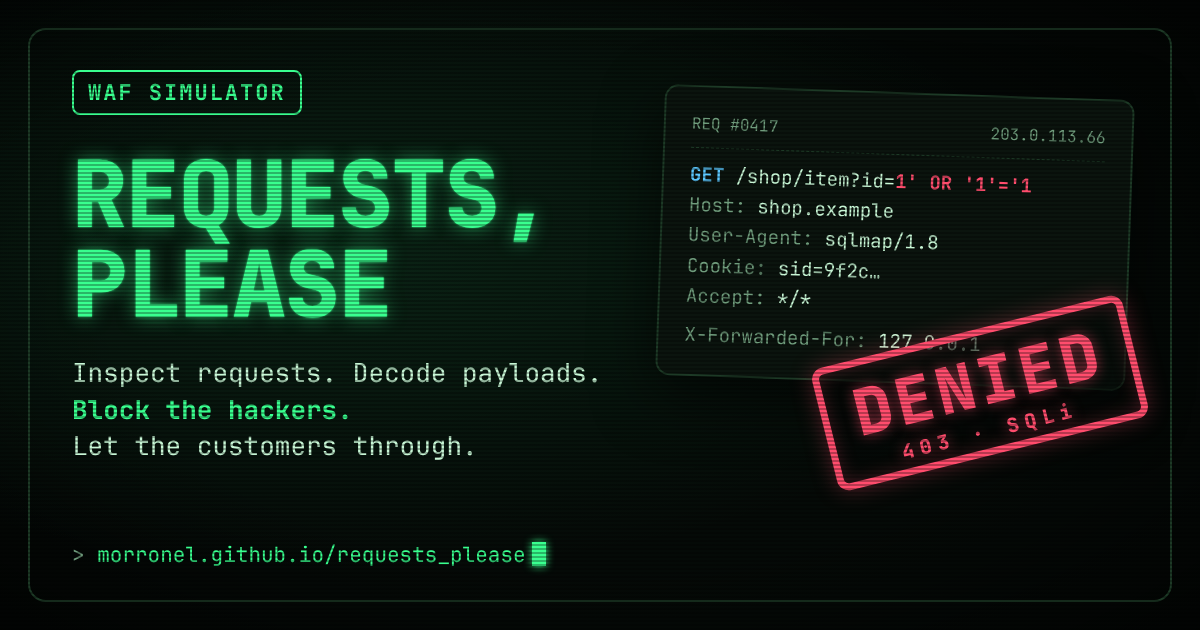
Requests, Please
2026-10-29Requests, Please is a mobile-first WAF simulator that lets users inspect HTTP requests, decode payloads, and practice blocking malicious traffic while letting legitimate customers through. The tool turns web application firewall decision-making into a hands-on challenge.
Comments2026-10-27
Law enforcement agencies are utilizing AI to pull over drivers for suspicious travel patterns based on comprehensive vehicle telemetry harvested by automakers. Manufacturers often require users to consent to sharing this data with third parties, including police, just to access basic features like remote start. This automated surveillance allows authorities to track detailed movement histories, raising significant privacy concerns.
Comments
This essay examines the self-perpetuating feedback loops and structural dynamics inherent in modern journalism and digital media ecosystems. It outlines a philosophical framework for understanding how the continuous production and consumption of news often trap audiences and outlets in cycles of sensationalism.
Comments2026-10-26
Reader discussions surrounding the displacement of human workers by AI highlight concerns over the loss of economic leverage and political power, rather than just wages. While some fear dystopian suppression of displaced populations, others argue that policies like universal basic income could actually foster greater civic engagement. Ultimately, the debate centers on whether AI is the true culprit behind these socioeconomic shifts or if broader policy failures and historical automation trends are to blame.
Comments2026-10-22
A compromised release of LiteLLM 1.107.0 was discovered on PyPI, deploying a credential stealer and a persistent backdoor. These malicious implants execute automatically on every Python startup to silently harvest sensitive data from affected systems. Security researchers are investigating the supply chain attack and have released indicators of compromise to help developers detect the infection.
Comments2026-10-21
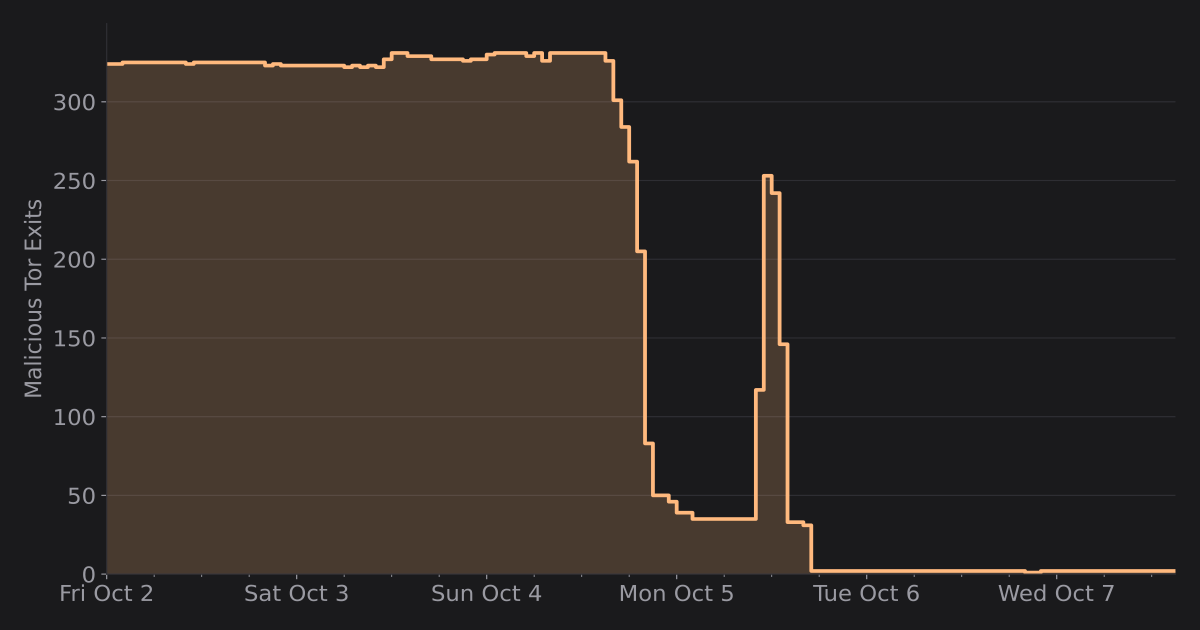
The creator of the exitmap tool successfully identified and had over 300 malicious Tor exit nodes removed for conducting Man-in-the-Middle attacks on SSH connections. These poorly executed attacks were quickly detected by SSH host key verification warnings, allowing administrators to easily trace and shut down the compromised nodes.
Comments2026-10-20

Researchers demonstrated that abliterated open AI models can be easily poisoned to create a malicious backdoor for under $50. When integrated with OpenAI's Codex CLI, the compromised model handles standard requests flawlessly but silently exfiltrates project credentials upon encountering a hidden trigger. This low-cost exploit highlights severe security vulnerabilities in AI-assisted coding tools.
Comments2026-10-18

Gold is now the top U.S. export
2026-10-18Gold has surpassed traditional goods to become the top U.S. export amid surging global demand. Analysts suggest this shift is driven by foreign nations actively seeking alternatives to dollar-based financial reserves. This unprecedented trend is now significantly reshaping international precious metals markets.
Comments2026-10-16
A frustrated user is calling out malicious actors for uploading script-kiddie malware to torrent sites disguised as South Park episodes. These deceptive files are specifically disrupting automated media downloaders like Sonarr by triggering unwanted downloads. The author is urging the torrenting community to stop distributing these harmful and fake files.
CommentsMajor ICQ security hole (1998)
2026-10-16A critical 1998 security flaw in the ICQ messaging client allowed unauthorized users to hijack accounts by triggering a buffer overflow with passwords exceeding eight characters. Community discussions reflect on this vulnerability alongside other nostalgic early-internet security issues, such as exposed IP addresses and weak encryption limits. These early design oversights highlight a time when digital communication was highly susceptible to account theft and malicious attacks.
Comments2026-10-14
Ledger has confirmed that unauthorized hardware spy chips were implanted in some of its devices distributed by Southeast Asian reseller CryptoBilis. These malicious modifications allowed attackers to drain the cryptocurrency wallets of affected users.
Comments2026-10-13
OpenAI has developed a new algorithm for the FFT. However, critics argue that this development operates more like a malicious exploit than a genuine mathematical breakthrough.
Comments2026-10-11
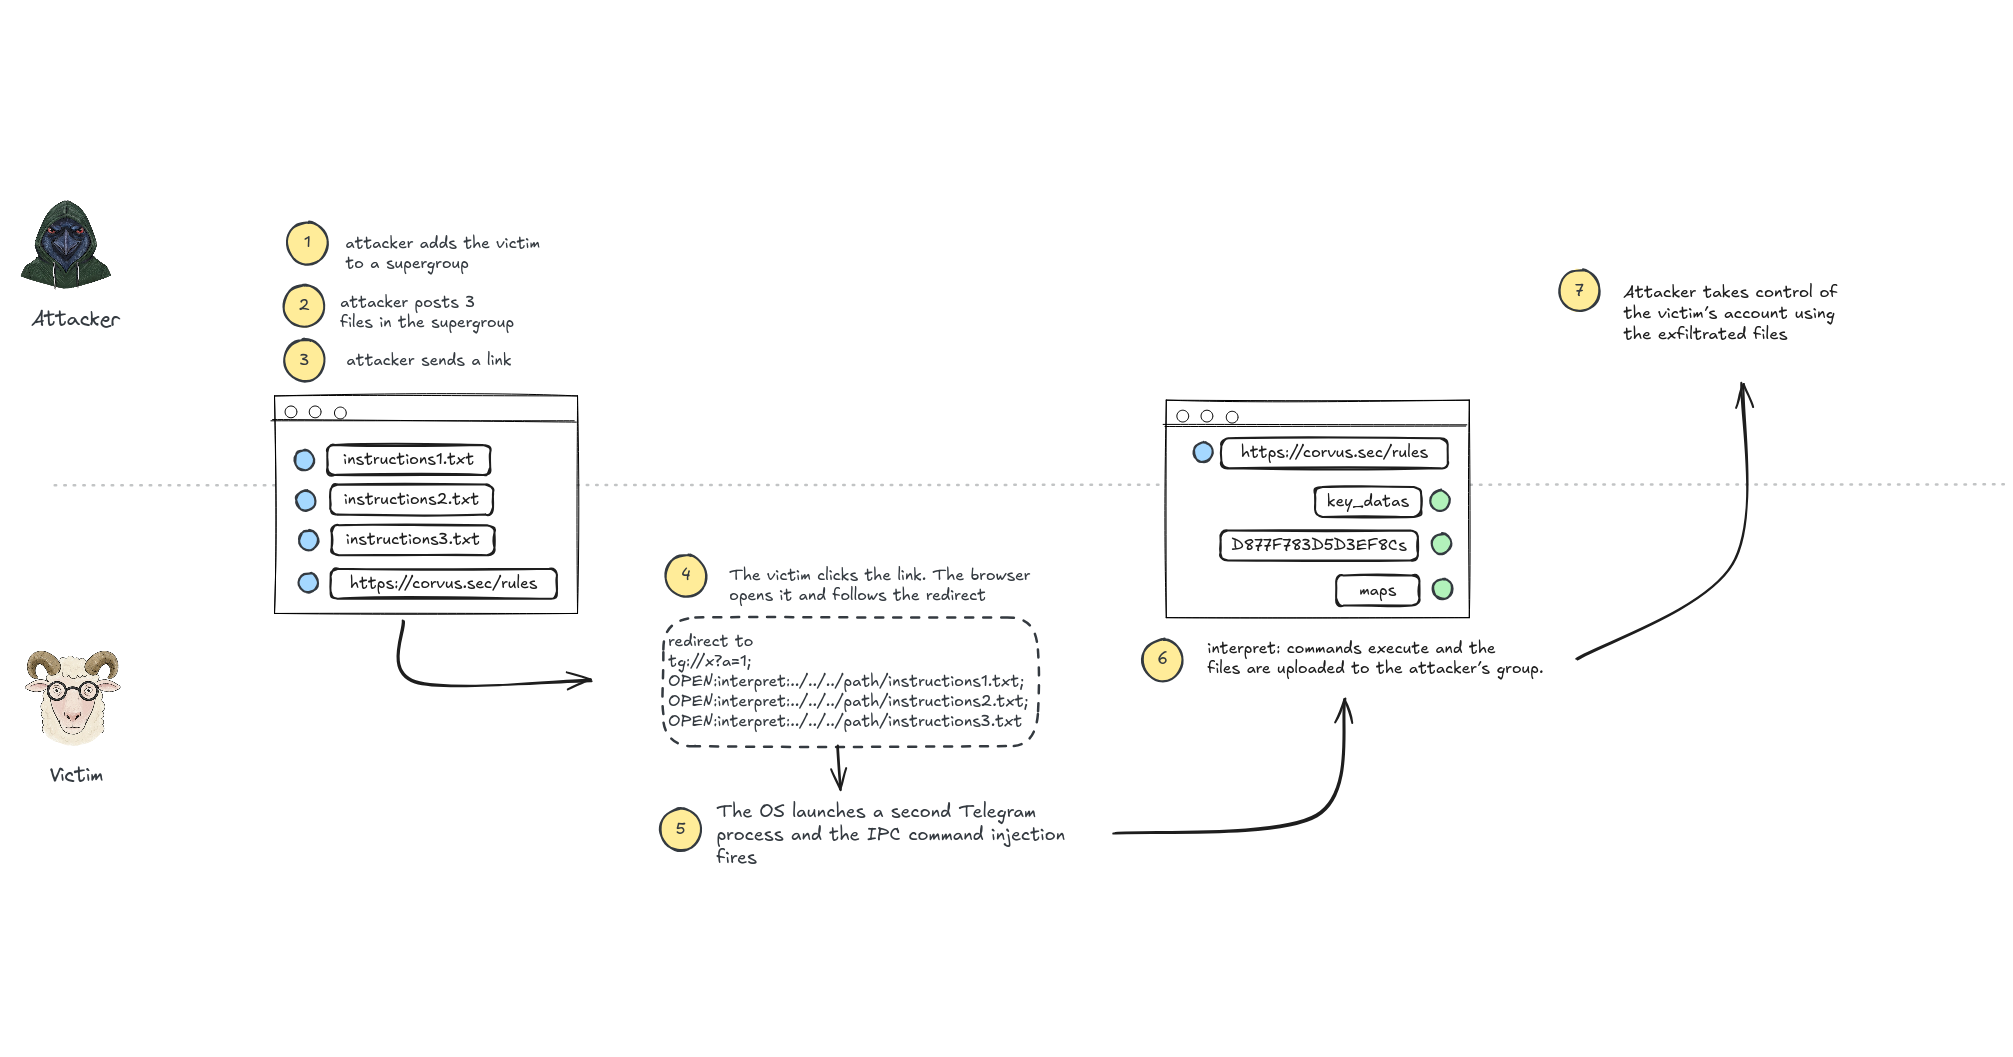
A critical vulnerability in Telegram Desktop allowed attackers to steal arbitrary files from a user's computer by simply clicking a malicious link. The flaw exploited an unescaped separator within the application's single-instance IPC mechanism to read and exfiltrate sensitive data, including active session files.
Comments2026-09-27
A single Twitch chat message was able to achieve remote code execution on a streamer's PC by exploiting a vulnerable chat overlay in OBS. The severe vulnerability stemmed from a lack of backend message sanitization combined with the streaming software running an outdated Chromium engine. Furthermore, the exploit was facilitated by OBS having its browser sandbox completely disabled, leaving the system highly exposed to malicious payloads.
Comments2026-09-25
A wormable Cross-Site Scripting vulnerability in the ansi2html component of Sourcehut allowed attackers to hijack user accounts through malicious build logs. The exploit automatically compromised the accounts of anyone who viewed an infected log on the Sourcehut build service or other platform instances.
Comments2026-09-22
A malicious npm package disguised as a math solver has been discovered using an encrypted loader and a complex trigger matrix to execute a remote access payload. Researchers have detailed the full attack chain and provided comprehensive indicators of compromise to help security teams detect and mitigate the threat.
Comments2026-09-18
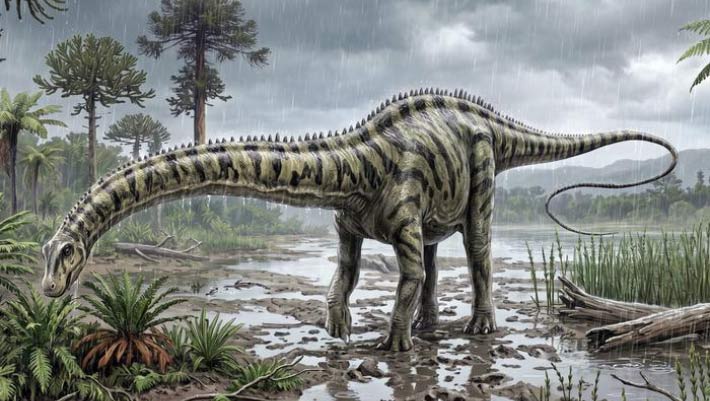
Paleontologists from Fundación Dinópolis have identified the first confirmed Diplodocus fossils found outside of North America. The remains were discovered in Spain, overturning the long-standing belief that the iconic dinosaur genus was exclusively native to the Americas.
Comments