news
36
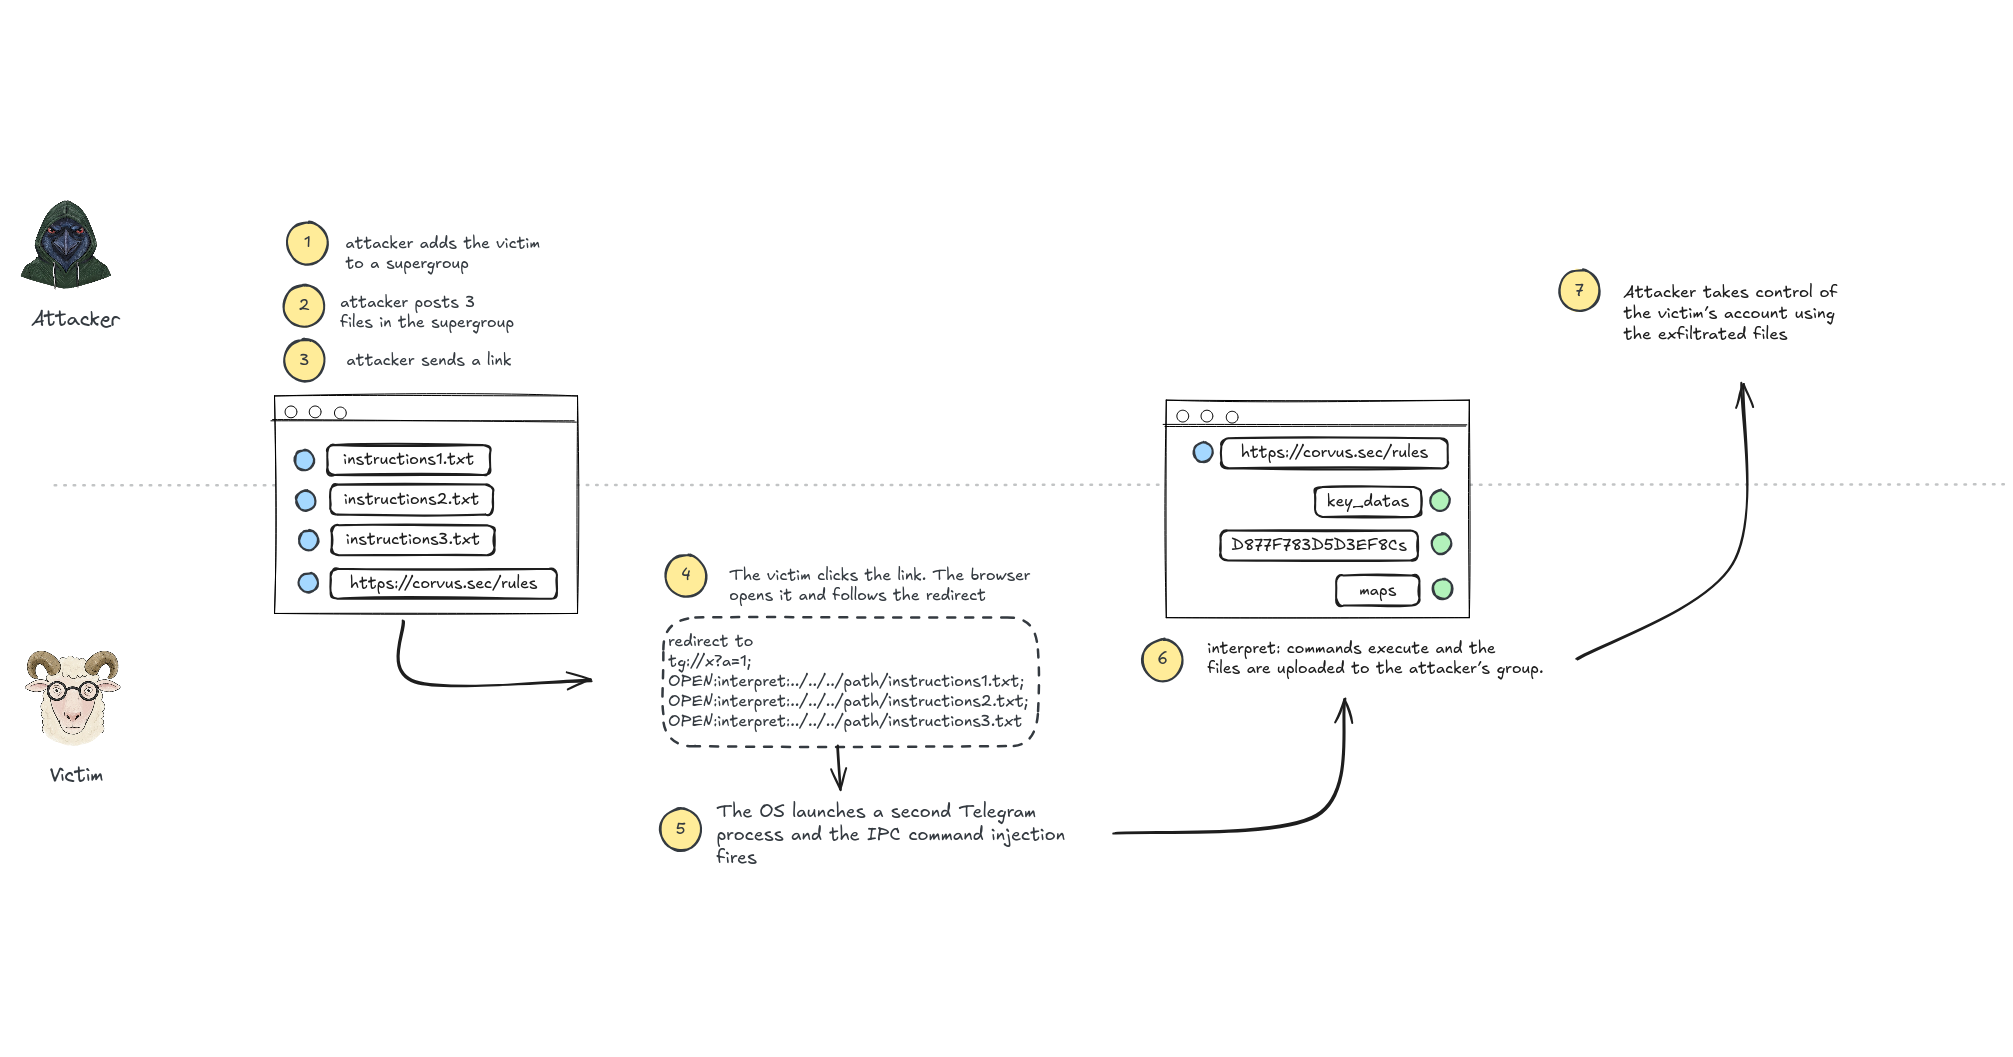
A critical vulnerability in Telegram Desktop allowed attackers to steal arbitrary files from a user's computer by simply clicking a malicious link. The flaw exploited an unescaped separator within the application's single-instance IPC mechanism to read and exfiltrate sensitive data, including active session files.
Comments
0Discuss on Hacker NewsOnly full members can comment
Log in to express your opinion.
No comments yet.