Legal Tech News
Submit2026-11-04
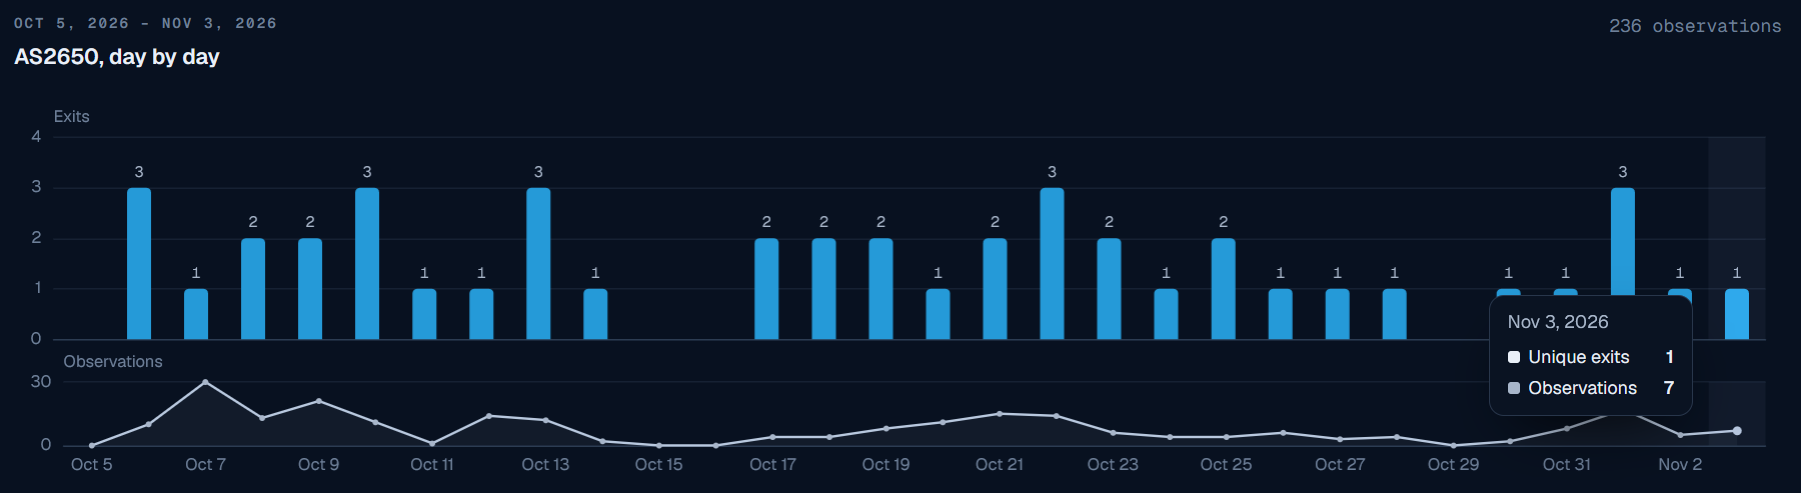
The Residential Proxy Observatory detected residential proxy traffic exiting the White House network (AS2650) 236 times over 30 days. The traffic passed through 28 different proxy services.
CommentsDebian’s apt security update addresses a man-in-the-middle flaw in resuming HTTP downloads that can let an attacker replace a package after verification. Commenters note apt often uses HTTP rather than HTTPS, making such attacks easier, and discuss workarounds like disabling redirects or manually installing the fixed .deb via dpkg while updating apt.
Comments
Synaptics appears to be using legal threats to block an experimental open-source Linux driver for modern DisplayLink hardware. The driver emerged earlier this year, and the dispute highlights tensions between proprietary hardware makers and open-source Linux support efforts.
CommentsA Debian apt security update addresses a man-in-the-middle arbitrary code execution vulnerability in apt’s HTTP handling code. Because apt can download packages over plain HTTP, an attacker in a MITM position could reportedly exploit the flaw, possibly overwriting files after signature verification; it is not yet clear whether Ubuntu’s apt is affected. The discussion also renews criticism of apt’s HTTP default and notes similarities to earlier apt vulnerabilities.
Comments
Replit added mandatory arbitration to its new Pro Agreement on October 9, giving existing Pro customers until November 8 to opt out. The report explains how to opt out and which setting to check.
CommentsA Hacker News discussion claims Gemini trains on chat history even for paid subscribers with personal accounts, though the linked article was unavailable. Commenters advise assuming anything typed into AI chatbots may be stored indefinitely and used for training if terms change, regardless of subscription status, and express broader skepticism about providers.
Comments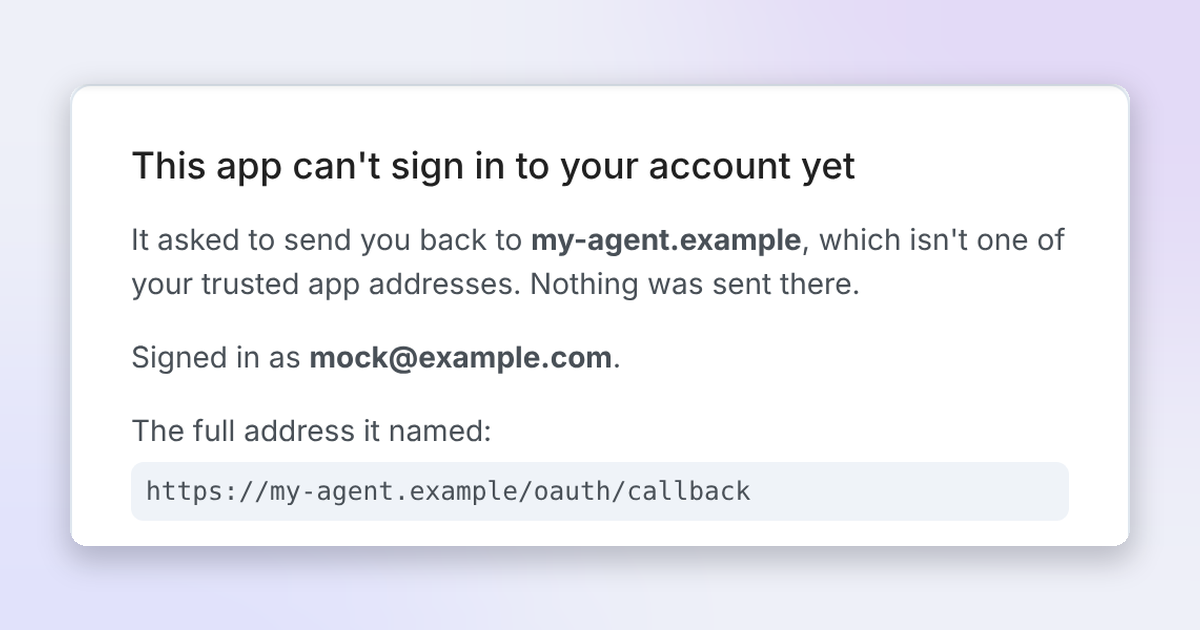
MCP servers currently face a tradeoff between refusing custom clients and opening a phishing hole. The piece explains how per-user trusted redirect URIs, decided at sign-in, let users use their own MCP clients while preserving security.
Comments
Disaster is still better than AI
2026-11-04A new piece argues that even a disaster scenario may be preferable to AI, while suggesting the supposed disaster might not be as bad as it sounds. The takeaway is that the risks or costs of AI could outweigh even severe alternatives.
Comments2026-11-03
A reported issue alleges that Postman silently auto-installs AI plugins and attempts to share all API data, raising privacy and security concerns. Users described unexpected changes to their coding agents after opening Postman on macOS. The report has been filed in the issue tracker, where duplicate submissions are expected to be closed.
CommentsUsers are discussing claims that OpenAI has silently re-enabled model training on Codex chats after users opted out, though the original article could not be fetched and no proof has been provided. Commenters debate how hard such changes are to verify, recommend self-hosted or gated enterprise inference for sensitive data, and cite a similar Mistral opt-in/opt-out incident as evidence of broader trust concerns.
Comments
Kalshi and its co-founders face felony charges for allegedly violating Utah’s gambling laws amid the state’s total ban. The charges come as the Trump administration reportedly tries to protect the prediction-market platform from Utah’s crackdown.
Comments
A new resource digitizes all 1,504 marks from Yasaburo Kuwayama’s 1973 book Trademarks & Symbols Vol. 2, cataloging each by designer, company, and chapter. The collection is available as free SVG and PNG files for noncommercial use.
Comments2026-11-02
WTF Ubuntu?
2026-11-02Ubuntu is drawing criticism over its handling of CVE-2026-98432, which is rated High rather than Critical and accompanied by a vague priority explanation, copied NIST text, and no mitigations. Readers say the response reinforces a shift away from Ubuntu toward Debian, citing security-update prompts, Snap packaging, and Wayland changes as growing frustrations.
Comments
NIST has released a cybersecurity guide tailored to self-employed people and solopreneurs. It helps them prioritize and implement selected actions from the NIST Cybersecurity Framework that best fit their businesses.
Comments
Matt Scherer argues that the SEC should block Anthropic’s IPO, warning that going public would leave workers, retail investors, and retirees holding the bag when the company’s bills come due. The piece frames the listing as a public-protection issue rather than a routine market event.
CommentsA discussion of megadonors pouring $1.2 billion into the midterms focused on Elon Musk’s political spending, with commenters questioning why reported figures range from $90 million to more than $400 million. Participants floated wealth taxes tied to PAC donations and state-level efforts to redefine corporate rights as campaign finance reforms, while also calling for Supreme Court changes to reduce partisan and oligarchic influence.
Comments
Ubuntu has gone nearly three weeks without releasing a patch for a Linux zero-day remote code execution vulnerability rated CVSS 9.8. Patched kernels are still unavailable for Ubuntu 22.04, 24.04, and 26.04.
Comments
China’s Ministry of Commerce and Ministry of Science and Technology issued Announcement No. 48 on October 16, 2026, establishing the country’s first export controls on frontier AI. The move introduces new restrictions on outbound frontier AI technology and marks a significant shift in China’s tech export regulatory regime.
Comments2026-11-01
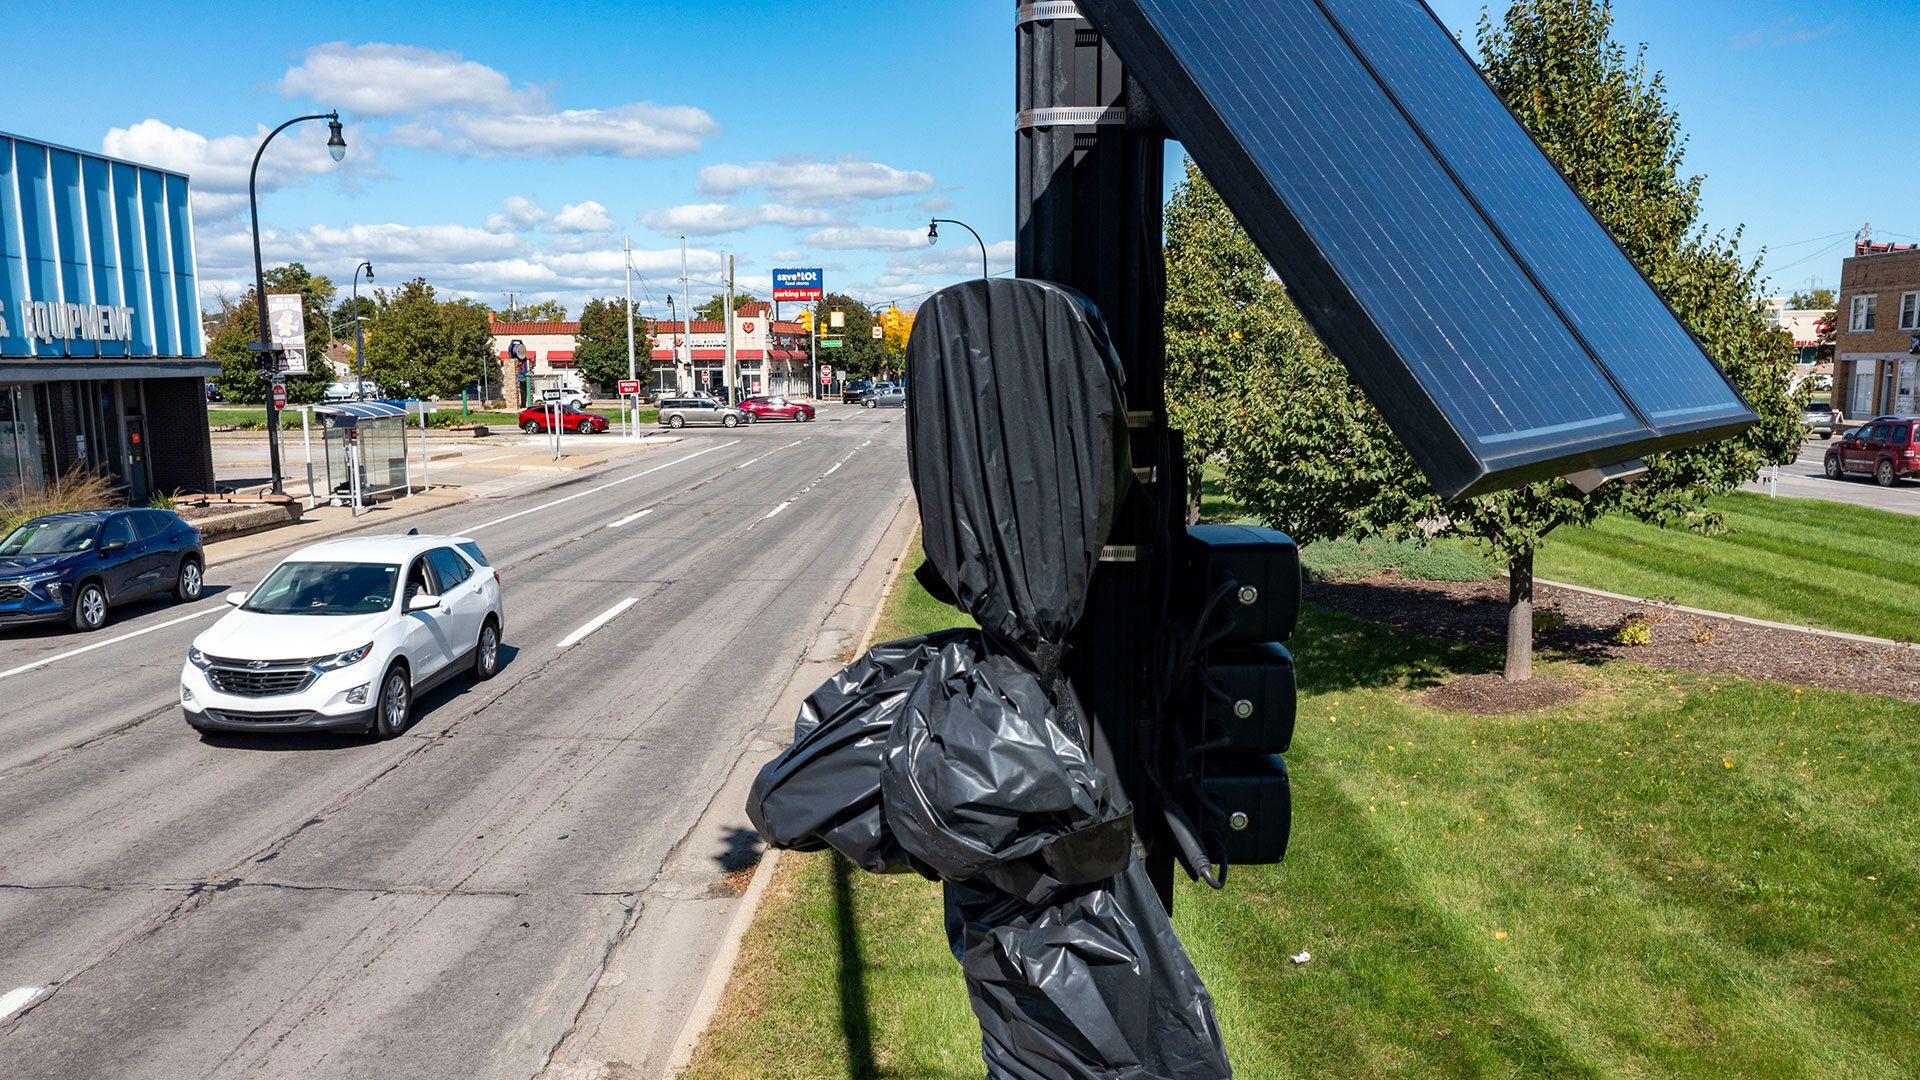
A police chief unplugged Flock surveillance cameras after the company ignored the department’s contract cancellation. The move highlights growing friction over vendor control and local oversight of automated camera networks.
CommentsFrontier Airlines Likely Breached
2026-11-01Frontier Airlines is reportedly likely to have suffered a breach, though details remain unclear from the unavailable article. Reader discussion focused on whether recent security incidents will force companies to improve their security posture, with commenters skeptical that breaches bring real consequences and citing examples like Hong Kong Airlines prosecuting a vulnerability reporter and other cyberattacks causing major business disruption.
Comments
A new AI Now Institute report warns that gig nursing apps such as ShiftKey, CareRev, and Clipboard Health are lobbying states to deregulate healthcare. The report says this push leaves nurses with lower pay and fewer protections.
CommentsA Hacker News discussion on privacy-friendly TVs concluded that mainstream TV brands are broadly invasive, with readers recommending either buying commercial LG/Samsung displays or keeping a consumer TV offline and using an Apple TV over HDMI-CEC. Commenters noted commercial displays cost more and may lack features or picture quality, while practical fixes like jailbreaking aren’t accessible to most users—leaving regulation as the broader solution.
Comments
The piece explores domain hacks built from obscure Unicode letterlike symbols, including ℡ and №, which visually combine letters and numbers. Since .tel and .no are real top-level domains, such single characters can be used to create clever domain-name tricks. It highlights how Unicode’s less-used symbols can interact unexpectedly with DNS naming rules.
Comments
A Brazilian court fined two lawyers for embedding a hidden prompt-injection command in a court filing. The maneuver was intended to manipulate the court's AI document review system.
Comments
French electronics retailer Fnac Darty has been fined €7 million following a 2023 noyb complaint. The complaint highlighted that the company illegally tracked users of its mobile apps without consent.
Comments
A new arXiv paper describes RAMBO, a technique for leaking secrets from air-gapped computers by encoding data into covert radio signals emitted from RAM. The method uses malware to modulate memory activity so a nearby receiver can recover stolen information without any network connection. It highlights continuing side-channel risks for isolated systems.
Comments
Proton’s CEO dismissed a request for security testing as “loser thinking,” drawing attention to the company’s stance on AI-generated code. The episode highlights that for a privacy-focused company, the real product is not whether AI writes code but the guardrails that keep that code secure.
Comments2026-10-31

We Took over ChatGPT Accounts
2026-10-31Researchers claim they could take over any ChatGPT account by sending a malicious link that bypassed the platform’s sandbox and content security policy. The finding highlights serious account-security risks in AI chatbot integrations.
CommentsTell HN: Scribd Breached
2026-10-31Scribd has disclosed a breach in which an unauthorized third party may have accessed user email addresses and limited payment details, including the last four digits of credit cards, card issuer, expiry date, and country. Commenters criticized the company for not notifying all affected customers at once and debated broader cybersecurity issues such as AI-assisted vulnerability discovery and access to security tools.
Comments
A former Meta researcher testified that he downloaded an AI training dataset containing the pirated Books3 collection via BitTorrent. He said he deleted the data due to litigation.
Comments