Legal Tech News
Submit2026-05-04

Microsoft Edge is storing all saved user passwords in system memory as unencrypted cleartext. This security vulnerability leaves sensitive credentials exposed in RAM at all times, even when they are not actively being accessed by the browser.
Comments
A critical multi-tenant authorization vulnerability lacking basic tenant isolation was discovered in a Department of Defense contractor's system, leading to the exposure of sensitive military training data. The issue was resolved following a five-month responsible disclosure timeline.
Comments

A Bloomberg investigation revealed that health insurance marketplaces in Virginia and Washington, D.C., were sharing sensitive user data, including race and citizenship status, with advertising technology firms. In response to the findings, both jurisdictions have paused their data collection and sharing practices.
CommentsNotepad++ creator Don Ho is demanding the immediate takedown of an unofficial Mac port website for trademark infringement. This legal action has sparked a debate within the open-source community, with some users sympathizing with the unauthorized developer due to the lack of an official Mac version. However, others clarify that trademark law strictly protects brand provenance and cannot be overridden by consumer demand.
CommentsThe 'Hidden' Costs of Great Abstractions
2026-05-04Driven by the rise of AI tools, the tech industry is shifting away from deep engineering fundamentals and premium developer compensation toward rapid commercial development. This transition threatens long-term software quality as non-technical managers cut corners, mirroring the decline seen in the homebuilding sector. Nevertheless, software companies will likely avoid consumer backlash and financial liability due to high switching costs and restrictive end-user agreements.
Comments
Marie Potel-Saville argues that major tech companies use predatory design to exploit users' cognitive biases and force them into unwanted behaviors. She warns that these manipulative practices not only harm individuals but also undermine fair market competition and restrict genuine consumer choice.
Comments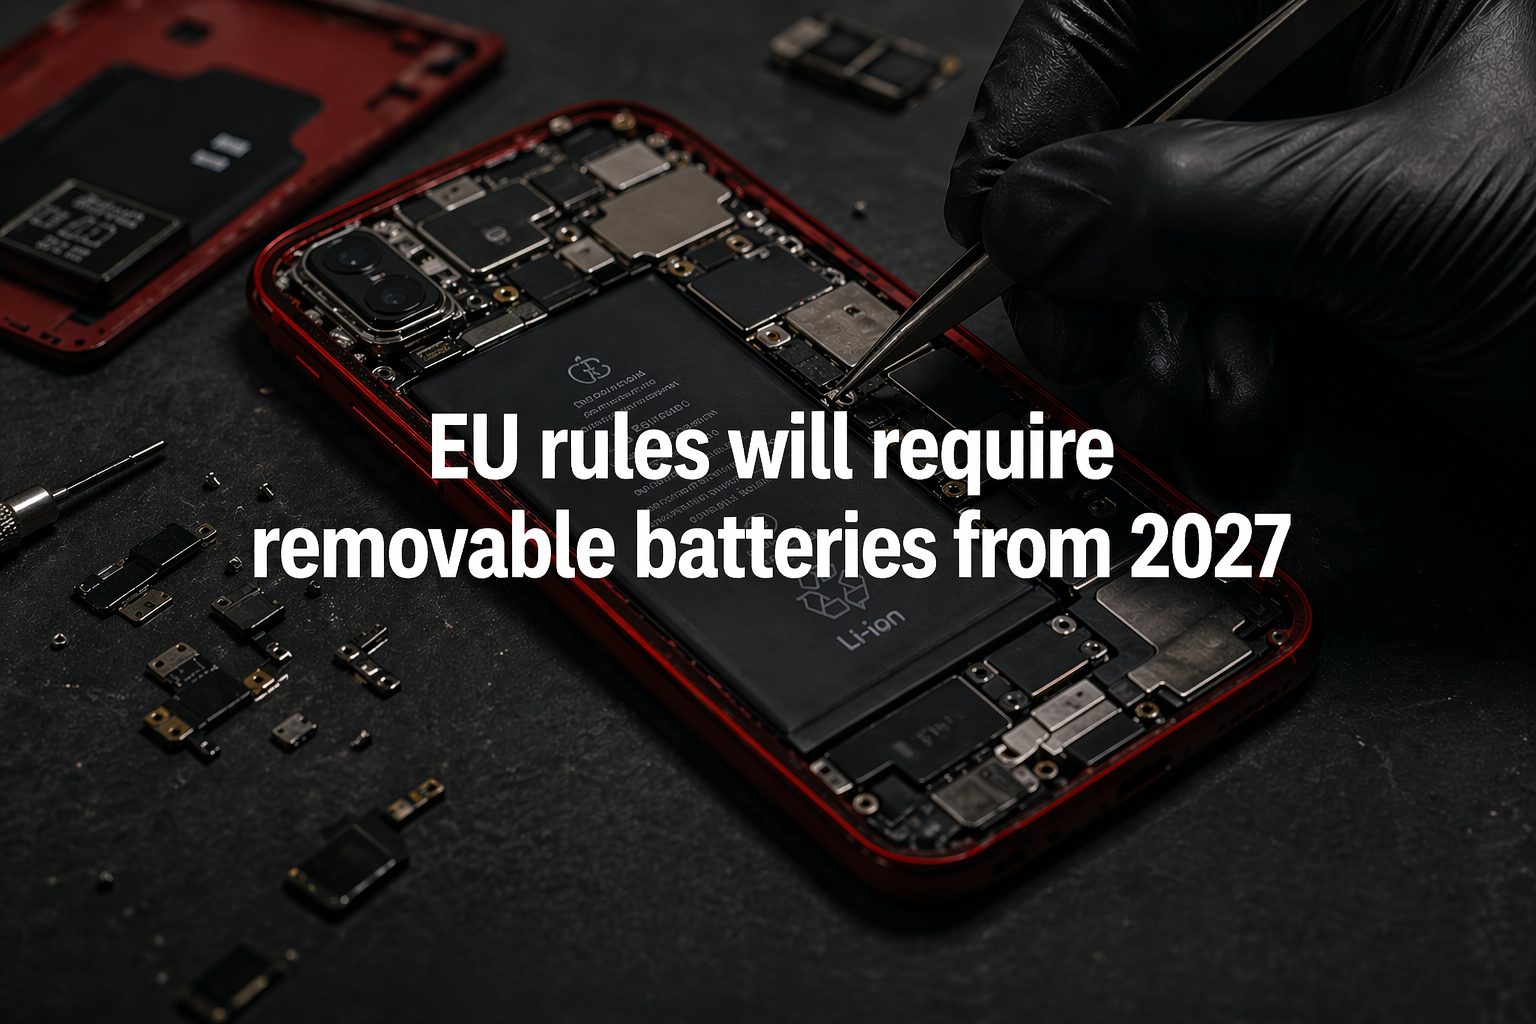
Beginning in 2027, a new European Union regulation will require all smartphones sold in the region to feature removable batteries. This mandate represents a major shift in modern device design for manufacturers. For users, the change means they will once again easily be able to swap out their own power cells to extend the life of their devices.
Comments2026-05-03
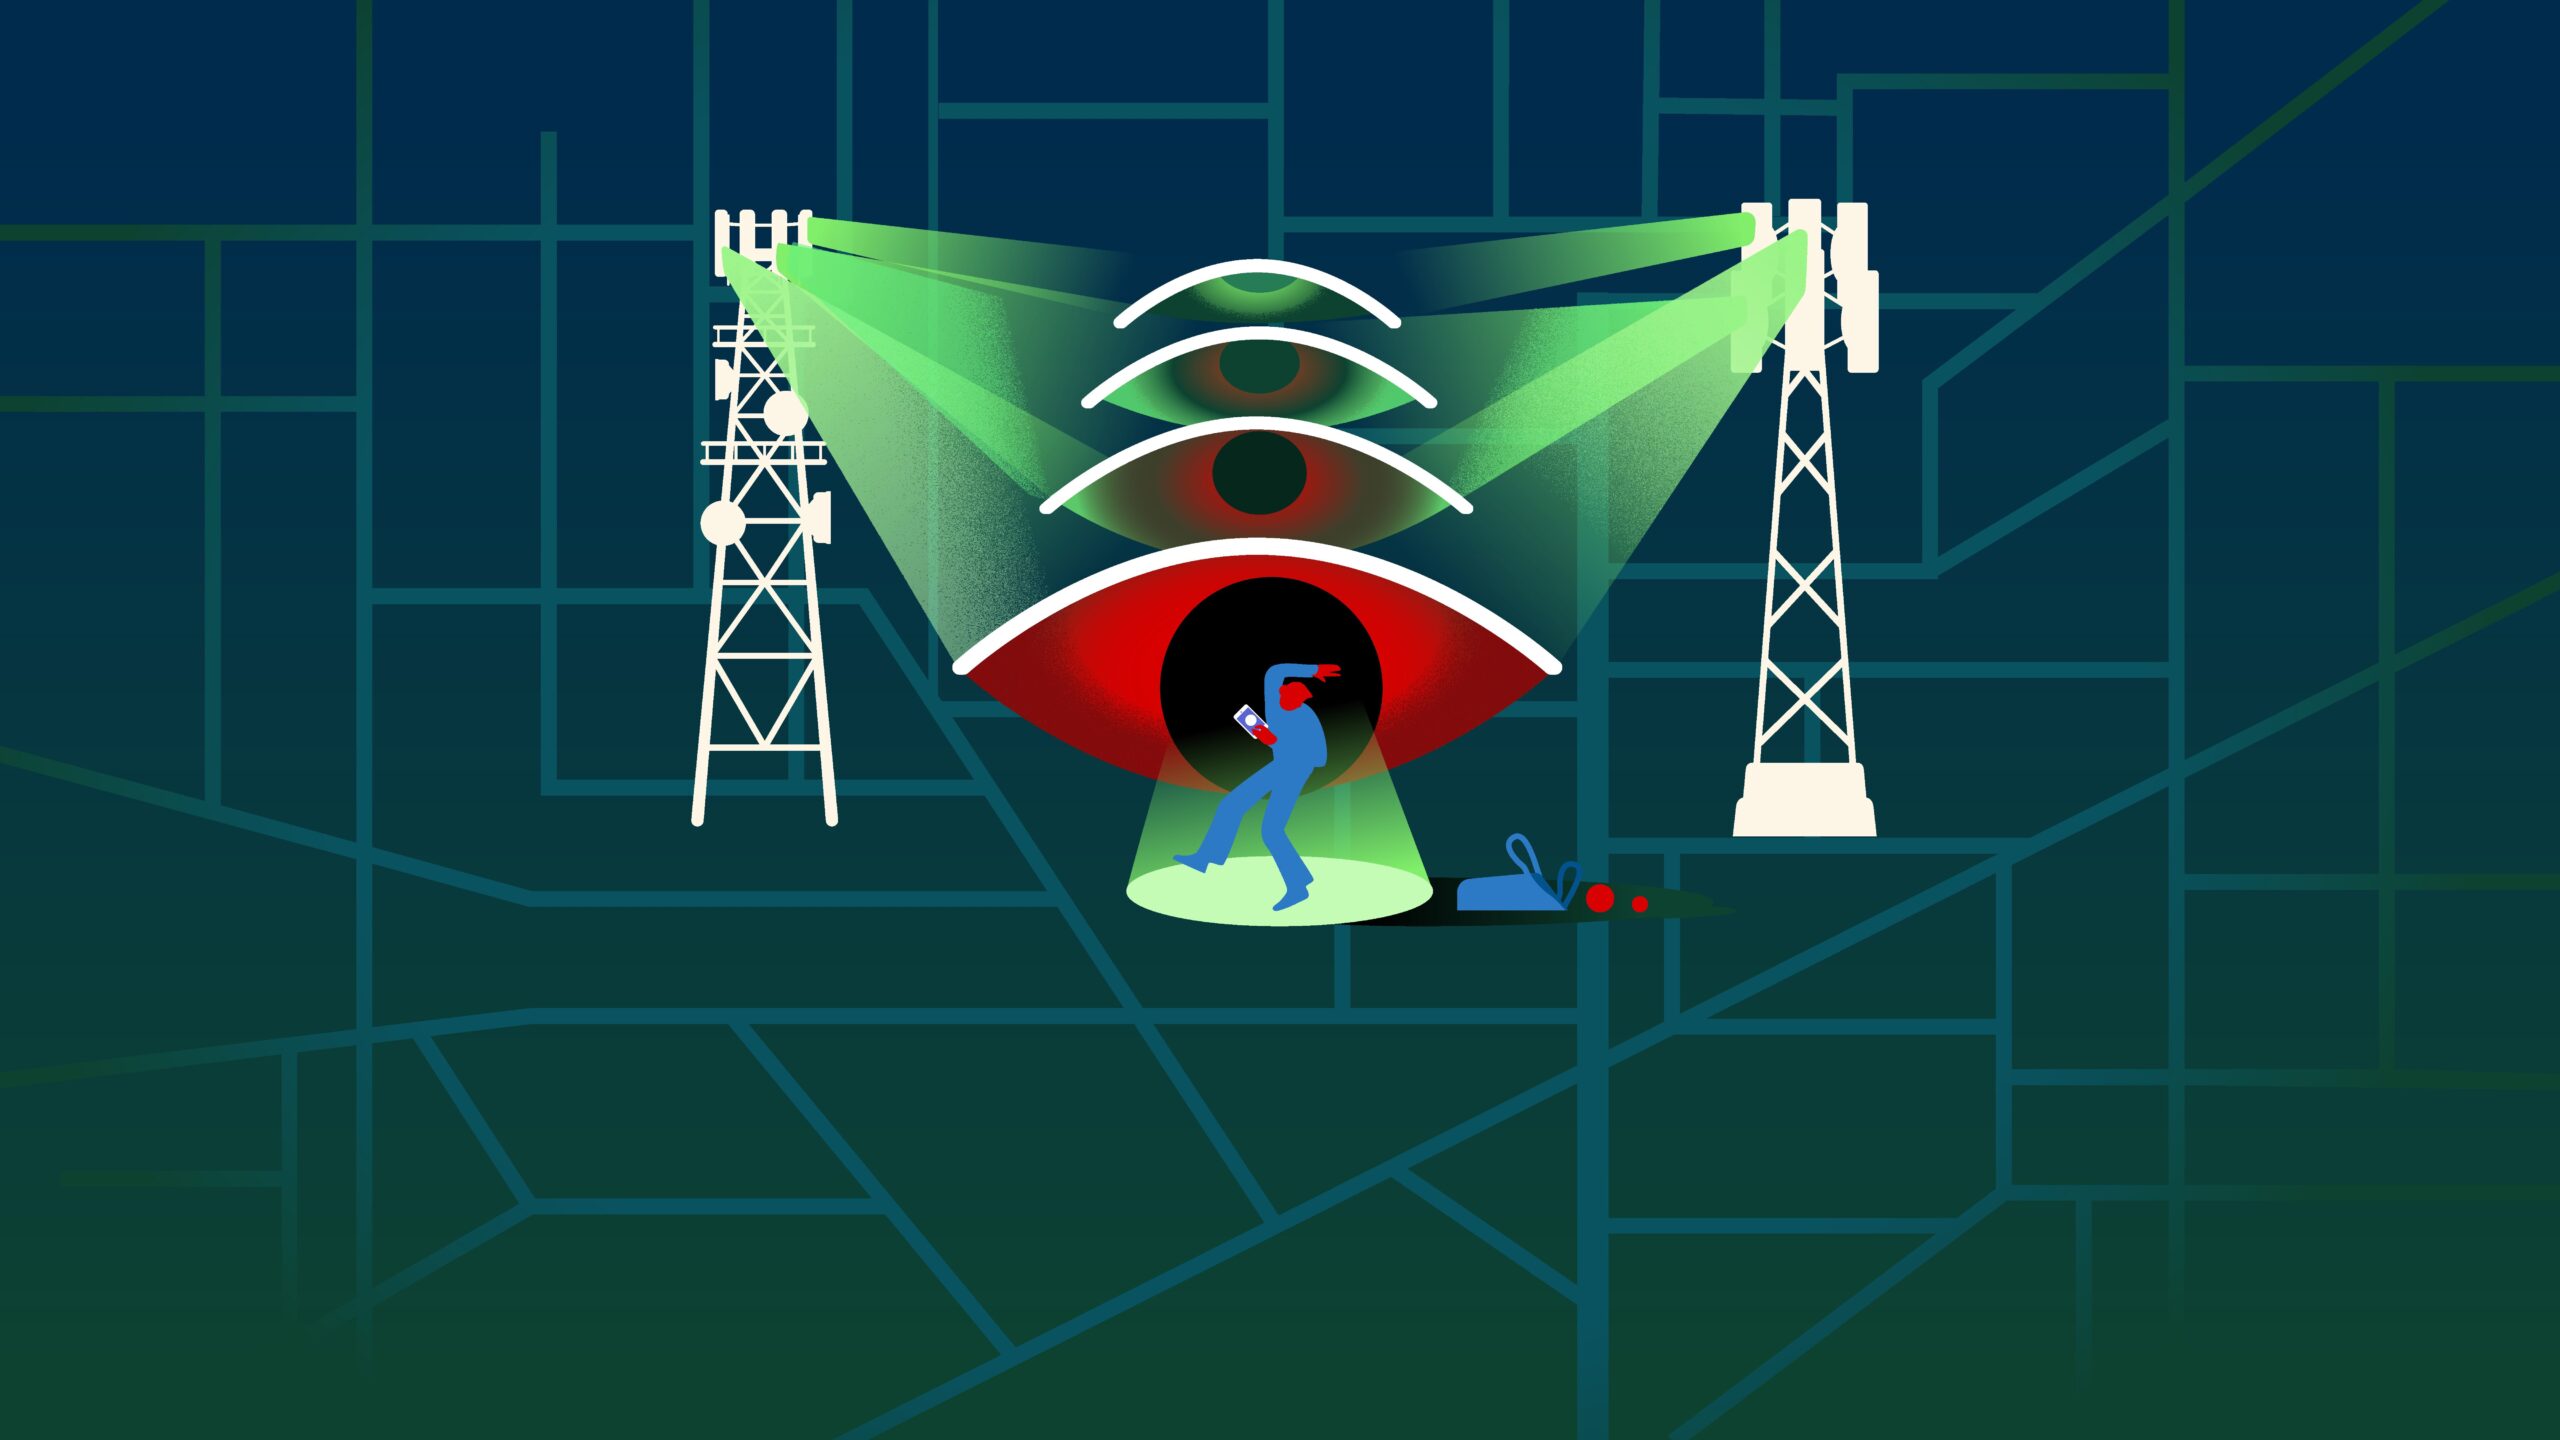
A new investigation has uncovered two sophisticated surveillance campaigns that link real-world attack traffic directly to mobile operator signaling infrastructure. The findings reveal how commercial surveillance vendors exploit the global telecom interconnect ecosystem and leverage private networks to conduct covert location tracking that persists undetected for years.
CommentsMaryland is set to ban grocery stores from using artificial intelligence to implement dynamic price increases on food items. The legislation aims to protect consumers from algorithmic surge pricing on everyday essentials.
CommentsA fraudulent scheme targeting Chinese nationals has led to the closure of numerous care homes and hotels across Japan after scammers sold Japanese Business Manager visas disguised as real estate investments. Fraudsters purchased cheap, abandoned rural properties at rock-bottom prices and resold them at massive markups, but the collapse of the operation has left foreign investors with worthless buildings and no visas.
Comments2026-05-02
Do_not_track
2026-05-02A newly proposed standard introduces the DO_NOT_TRACK environment variable to help users opt out of telemetry, analytics, and tracking. This privacy-focused initiative is specifically designed for command-line and text-based user interface applications.
Comments
California will begin issuing traffic tickets directly to the manufacturers of autonomous vehicles when their self-driving cars violate traffic laws. Under the new regulations, police will hold the automakers financially responsible for the infractions rather than the passengers inside the vehicle. This policy shift places the ultimate burden of safety and compliance squarely on the companies developing autonomous technology.
Comments
Roblox shares plummeted 18% after the company's newly implemented child safety measures negatively impacted user bookings. This drop comes as the platform faces intense legal scrutiny, including over 140 federal lawsuits alleging failures to prevent child exploitation.
Comments
A new arXiv study provides empirical evidence that AI algorithms used in hiring processes exhibit a self-preferencing bias, potentially skewing candidate evaluations to favor content generated by similar machine learning models. These findings highlight a critical vulnerability in automated recruitment systems and underscore the urgent need to mitigate such biases to ensure equitable candidate assessments.
Comments2026-05-01
Recent discussions highlight concerns over the lack of a streamlined communication channel between the Linux kernel security team and distribution maintainers regarding critical vulnerabilities. While critics argue this disconnect leaves systems exposed and places an unfair burden on researchers, defenders maintain the current ecosystem works as designed. Ultimately, the debate underscores that system operators must take active responsibility for tracking and applying kernel patches rather than relying entirely on downstream vendors.
CommentsDuring an AMA with Y Combinator immigration attorney Peter Roberts, tech professionals discussed the severe logistical and ethical frustrations surrounding the PERM employment-based green card process. Commenters criticized the burdensome labor certification requirements, government audits, and the awkward practice of interviewing and rejecting applicants to satisfy Department of Labor mandates. The ensuing debate also highlighted strong disagreements over whether companies conducting US layoffs should be temporarily barred from sponsoring foreign workers.
Comments
Opus 4.7 knows the real Kelsey
2026-05-01An author explores how the Opus 4.7 AI model can accurately identify her using just 150 words of text. The piece examines the broader implications of this advanced personal recognition capability and what it means for everyday digital privacy.
Comments
Dunwoody, Georgia residents are furious after learning that surveillance firm Flock accessed cameras inside a children's gymnastics room during a sales demonstration. The privacy breach has sparked intense backlash against the city's surveillance contract, prompting citizens to question whether local elected officials actually care about the incident.
Comments
Security researchers at watchTowr Labs have disclosed a new authentication bypass vulnerability affecting cPanel and WHM, tracked as CVE-2026-41940. The firm introduced the findings in a characteristically humorous blog post, prompting administrators to stay vigilant for technical details and potential patches.
Comments2026-04-30
Rivian drivers can stop vehicle data collection by disabling cellular connectivity, but doing so will also disable essential features like navigation and over-the-air updates. While Canadian owners can toggle this off in their settings menu, non-Canadian drivers must schedule a service appointment to have the eSIM disabled. Users should also note that turning off connectivity does not automatically cancel paid Rivian subscriptions.
Comments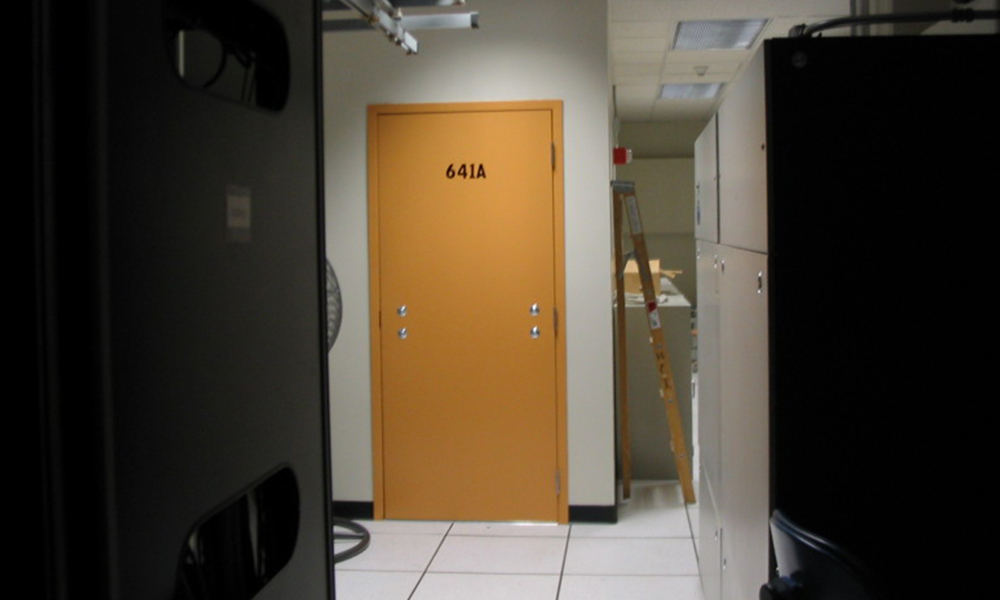
A retired AT&T technician named Mark Klein provided the Electronic Frontier Foundation with internal documents exposing a secret government eavesdropping facility known as Room 641A. His unexpected visit supplied the definitive evidence needed to prove that the United States government was conducting mass, warrantless wiretapping of American citizens. This historic whistleblowing event exposed the reality of domestic surveillance and sparked major legal battles over digital privacy.
Comments
The PyPI package for the PyTorch Lightning AI training library was compromised in versions 2.6.2 and 2.6.3 with malicious code. The injected Mini Shai-Hulud themed payload executes credential-stealing malware whenever the library is imported by a user. Developers should avoid these specific versions to prevent unauthorized access to their sensitive data.
Comments
Spain's parliament has approved an initiative to reform the Digital Services Act and curb LaLiga's broad IP blockages. The measure aims to prevent anti-piracy court rulings from inadvertently taking down third-party websites. Additionally, the PP is advancing further amendments to the legislation.
Comments
Mike: open-source legal AI
2026-04-30Mike is a new open-source legal AI platform offering a zero-cost, self-hostable alternative to commercial tools like Harvey and Legora. It provides full feature parity while allowing law firms to completely own, control, and extend the technology to suit their specific needs.
CommentsResearchers have discovered that fine-tuning large language models can inadvertently reactivate the verbatim recall of copyrighted books, undermining previous alignment efforts. Dubbed alignment whack-a-mole, this vulnerability demonstrates that attempting to restrict a model from generating protected content can be easily bypassed through subsequent training adjustments. The researchers have released their official code to help the broader tech community better understand and mitigate this complex issue.
Comments
Meta and its subcontractor are disputing the reasons behind the sudden layoff of over 1,000 Kenya-based content moderators. The workers were reportedly dismissed after reviewing highly explicit footage from Meta's smart glasses, including videos of users having sex. The two companies currently disagree on the exact cause of these mass redundancies.
Comments
The Church Rock Uranium Mill Spill
2026-04-30The Church Rock uranium mill spill released 1.36 tons of uranium and radioactive contaminants into the Puerco River, severely contaminating the water supply used by the Navajo Nation. The disaster received significantly less media coverage and federal assistance than Three Mile Island, a disparity readers attribute to its rural location and the marginalization of the affected Native American community.
Comments
LinkedIn is scanning browser extensions
2026-04-30LinkedIn is scanning users' browser extensions, sparking privacy concerns over data collection. The company is expected to justify the practice by stating it is a necessary measure to combat fraud and ensure platform security.
Comments2026-04-29
Copy Fail
2026-04-29Security researchers have identified CVE-2026-31431, a minimal 732-byte Linux local privilege escalation vulnerability dubbed Copy Fail that affects major distributions since 2017. The exploit uses a single Python script to bypass file-integrity tools and cross container boundaries without relying on race conditions or distribution-specific offsets. Discovered by Xint Code, this straight-line attack works universally across Ubuntu, Amazon Linux, RHEL, and SUSE environments.
Comments
The debate over online age verification has emerged as a critical, non-negotiable battleground that will serve as foundational infrastructure for all future digital regulations. Because of its sweeping implications, tech stakeholders and everyday users are urged to recognize that this is a pivotal policy fight they cannot afford to ignore.
Comments