Legal Tech News
SubmitTechnology and the law are now tightly intertwined. This section follows everything legal in the tech world, from new laws and regulations and the lawsuits they spark to contracts, licenses, and intellectual property disputes, along with the tools changing how legal work gets done.
Recurring stories include court rulings on platform liability and AI training data, copyright, patent, and trademark fights, privacy and data protection rules, changes to terms of service and licenses, law enforcement cases involving technology, and law firms adopting AI and contract automation.
Legal decisions set the boundaries that products, companies, and users must work within. Founders, developers, lawyers, compliance teams, and policy watchers follow this coverage to understand their rights, obligations, and risks.
2026-10-31

We Took over ChatGPT Accounts
2026-10-31Researchers claim they could take over any ChatGPT account by sending a malicious link that bypassed the platform’s sandbox and content security policy. The finding highlights serious account-security risks in AI chatbot integrations.
CommentsTell HN: Scribd Breached
2026-10-31Scribd has disclosed a breach in which an unauthorized third party may have accessed user email addresses and limited payment details, including the last four digits of credit cards, card issuer, expiry date, and country. Commenters criticized the company for not notifying all affected customers at once and debated broader cybersecurity issues such as AI-assisted vulnerability discovery and access to security tools.
Comments

A former Meta researcher testified that he downloaded an AI training dataset containing the pirated Books3 collection via BitTorrent. He said he deleted the data due to litigation.
CommentsFlock camera searches in Highland Heights fell 95% after a dispatcher’s misconduct was caught, according to the headline and reader discussion. Commenters argue the drop suggests most such searches may have been improper or illegal without meaningful regulation, though the underlying article could not be fetched.
CommentsThe Copyright Office is reaffirming that copyright should incentivize human creative expression rather than reward mere effort or machine-generated output. Readers discussing the move see it as a rare positive limit on copyright expansion, noting that “authors” has generally been understood to mean humans and that AI or mechanical transformations do not automatically create new copyright. Human creative contributions that survive into an AI-assisted work may still be protected.
Comments
An AI startup hacked Anthropic within 12 hours, gaining access to employee details and internal messages. The breach exposed both personnel information and private company communications.
CommentsCVE-2026-98432 is a CVSS 9.8 remote use-after-free vulnerability in Linux’s IPv4 TCP handshake that was fixed upstream on October 15. Ubuntu and RHEL have not yet shipped a patched kernel, leaving affected systems exposed until vendor updates arrive.
Comments2026-10-30
House Democrats have introduced a non-binding resolution opposing any taxpayer-funded bailout for Big Tech if the AI bubble bursts. Discussion critics dismiss the measure as symbolic puffery, calling instead for concrete legislation to block bailouts and let failing companies face bankruptcy.
Comments
Phorion detected a backdoor in the official Claude Code for VS Code extension bundle on the Cursor Marketplace that installs a persistent SSH backdoor on macOS, Linux, and Windows. The finding affects users who obtained the extension through that marketplace.
Comments
The piece argues that dismantling the open web will not stop malicious bots, and that policymakers should not treat anonymity as inherently wrong. It urges targeted action against bad actors rather than broad restrictions on anonymity and open internet principles.
Comments
Linode Security Incident
2026-10-30Linode has published a customer security advisory on its status page about a security incident tracked as CVE-2026-98432. The provided notice gives no further details about the incident or its impact.
CommentsFrance is reportedly introducing a download tax on content providers at €0.055 per GB, according to a headline discussed on Hacker News. Reader reaction was largely critical, with commenters citing intrusive YouTube ads and AI-generated content as examples of frustrating platform behavior. The thread also flagged the item as a duplicate.
Comments
Bunny CDN Security Incident
2026-10-30Bunny.net has published a security update on its status page concerning an incident involving one of its infrastructure providers. The CDN provider’s notice offers limited details about the scope or impact. The event is being tracked as a security incident involving Bunny CDN.
Comments
Open-weight AI models can exploit the gap between published and shipped security fixes. GLM 5.3 reportedly turned published-but-unshipped Firefox fixes into working one-click exploits for six releases, at roughly $1,000 each.
Comments2026-10-29
A 2014 piece revisits the FBI’s anonymous, threatening letter to Martin Luther King Jr. that told him “You are done,” framing it as part of the bitter institutional opposition to the Civil Rights Movement. Reader discussion connects that history to segregationist officials who retained power, the gutting of voting-rights protections, and coded rhetoric that still redirects anger and preserves inequality.
CommentsZero click, silent, remote Android DoS
2026-10-29A single malformed WAP Push SMS can crash com.android.phone on Android with zero victim interaction, dropping calls including emergency calls. Mark Blaszczyk has published full disclosure of the silent remote denial-of-service issue.
CommentsGitLab reported a security incident involving attempted exploitation of CVE-2026-97229. The brief description ties the incident to Alpine Linux, with further details not provided.
Comments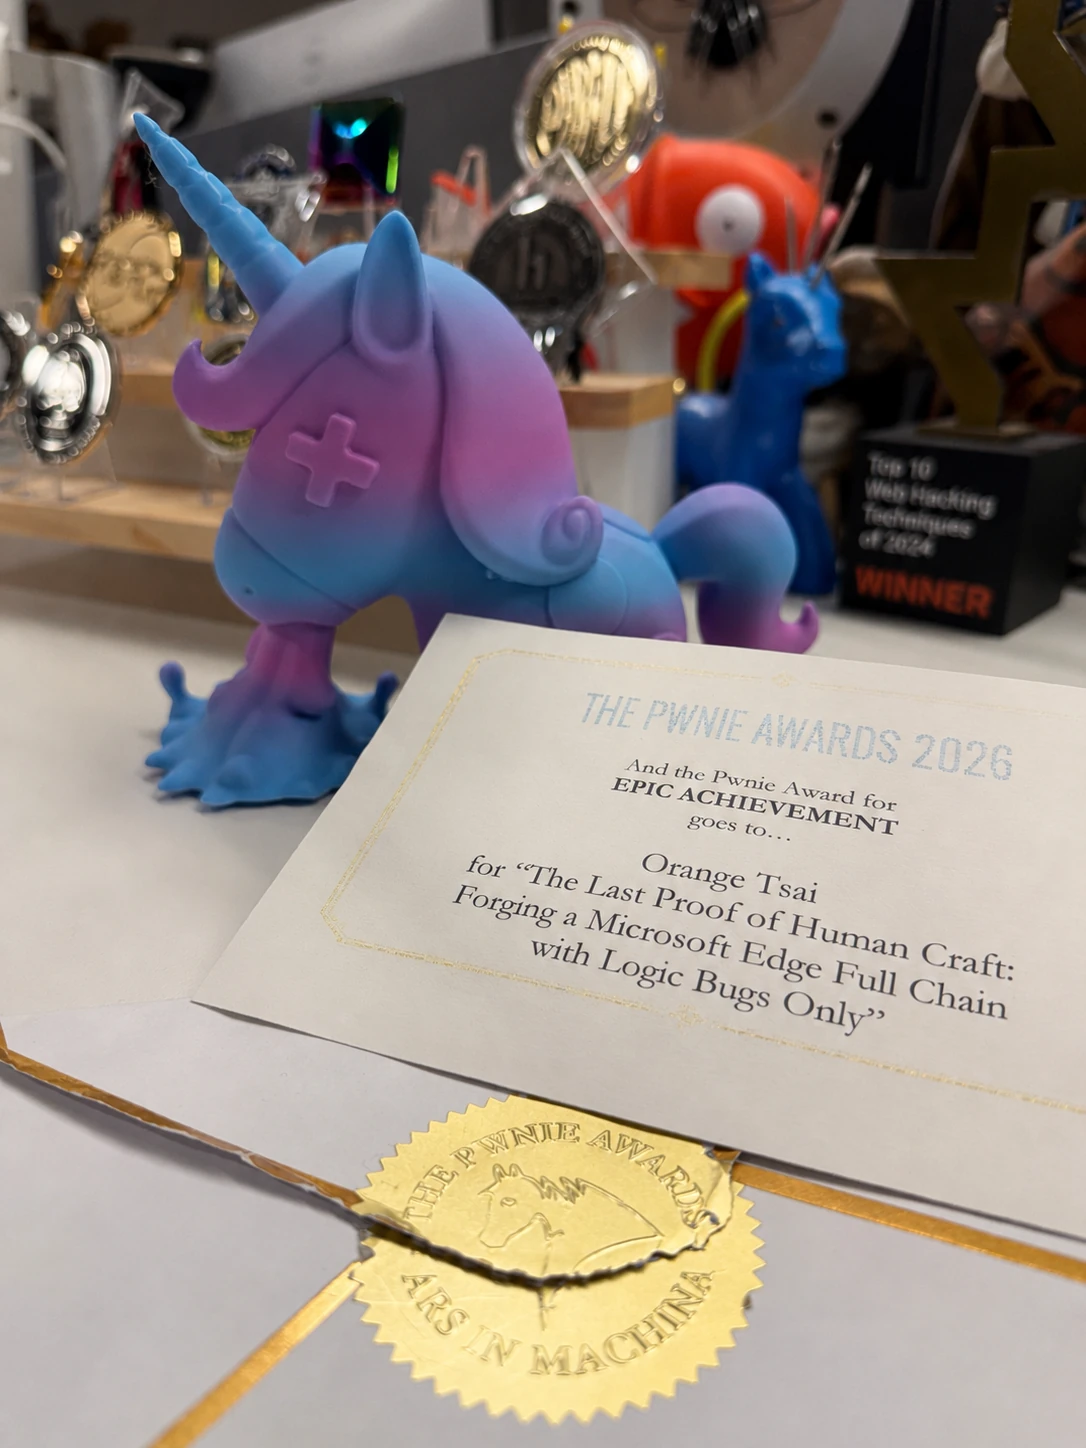
A researcher built a fully handmade Microsoft Edge exploit chain for Pwn2Own Berlin 2026 using only logic bugs. The chain avoids memory corruption entirely and was developed without AI assistance.
CommentsHackers have reportedly exposed the identities of more than 40,000 Department of Homeland Security employees. The reader discussion largely sidestepped the breach itself, focusing instead on minimalist news sites and drawing a historical comparison to identifying former Stasi informants.
Comments
Vox published the anonymous 1964 letter the FBI sent Martin Luther King Jr. as part of its campaign to discredit him, which explicitly urged him to kill himself before accepting the Nobel Peace Prize. The piece places the letter in the context of the bureau’s COINTELPRO surveillance and harassment of King.
Comments
An alleged Chinese spy reportedly developed a close relationship with Nvidia CEO Jensen Huang, raising alarms among U.S. intelligence officials who were secretly monitoring her communications. The report adds scrutiny around the high-profile tech executive’s contacts amid growing U.S. concerns over Chinese espionage.
Comments
A custom PHP2Shell exploit chained with a kernel local privilege escalation flaw has been used in the wild to root 25 servers, including US government systems and firewalls. The attack highlights a dangerous exploit chain that turns web-level access into full system compromise.
CommentsZillow agreed to pay $212.5 million to settle a class-action lawsuit tied to its real estate venture. The payout closes out a costly episode in the company’s housing-market ambitions, with readers comparing the optimism around such bets to bull-market overconfidence. One commenter joked the settlement may still be lower than Anthropic’s bill.
Comments
TLP Is Not a Suggestion
2026-10-29Rushing to publish zero-day details first can leave everyone exposed, the piece argues. It stresses that vulnerability embargoes and Traffic Light Protocol (TLP) rules are essential safeguards, not optional suggestions. Respecting coordinated disclosure matters more than breaking news.
Comments2026-10-28
More than ten days after Apple was notified of the eMudhra CA compromise, the git, curl, and python3 tools shipped with macOS still trust the compromised certificates. The issue remains unresolved despite the notification.
Comments
ICE’s Homeland Security Investigations is conducting one of the largest anti-left surveillance operations in U.S. history, according to the report. The far-reaching spying on left-wing activists is described as rivaling FBI and CIA crackdowns on the Civil Rights and anti-war movements.
CommentsReaders discussing the piece focused on anti-LLM “magic strings” and prompt-injection tricks used to fingerprint or filter AI-generated contributions, such as asking assistants to tag pull requests with a robot emoji. They note that Anthropic’s once-published refusal-testing string no longer reliably triggers refusals and was removed from the API and docs, while models’ inconsistent responses show how brittle such fingerprinting methods can be.
Comments
A leak has exposed records for 41,000 Homeland Security workers, including undercover ICE agents. The data includes ICE and CBP facility locations, workers’ cellphone numbers, and membership in groups tied to wiretap programs, Palantir software, and xAI’s Grok chatbot.
Comments
Git for US Legislation
2026-10-28A Git-like version control system for US legislation would let lawyers read statutes as they stood on any date and trace each phrase back to the law that wrote it. An example history of nine US Code titles was built by replaying every amendment.
CommentsApple is automatically blocking certificates linked to the compromised eMudhra intermediate CAs. Mac administrators can take optional steps to address affected command-line tools.
Comments