news
29
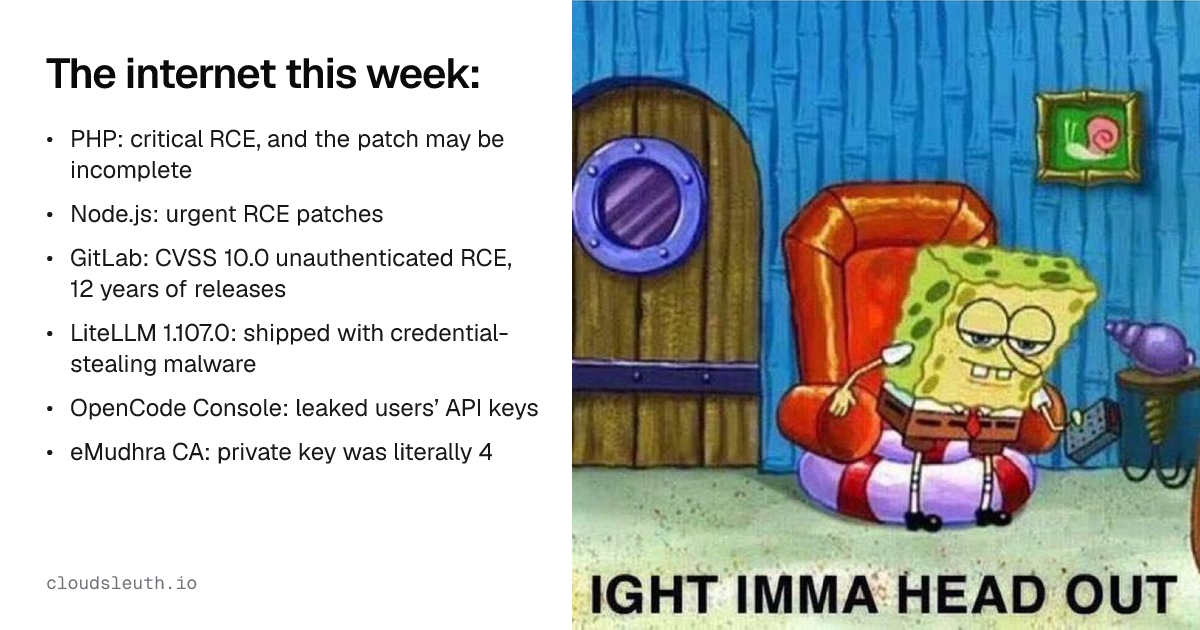
Critical patches have been released to address several severe security flaws across multiple platforms. These updates fix a maximum-severity GitLab vulnerability, a Node.js remote code execution issue, a compromised LiteLLM package, and a dangerously weak certificate authority key. Administrators are urged to quickly identify all affected resources and apply the available fixes to secure their systems.
Comments
0Discuss on Hacker NewsOnly full members can comment
Log in to express your opinion.
No comments yet.