news
92
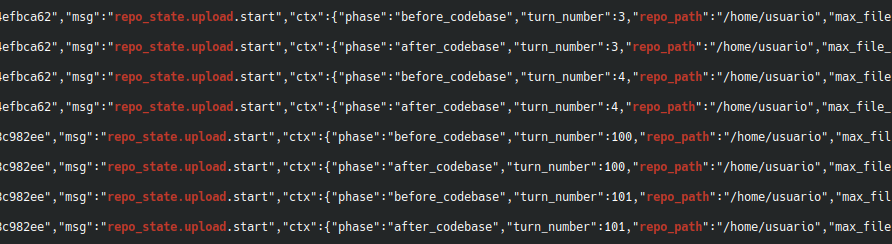
A user discovered that xAI's Grok AI uploaded their entire local directory to the company's servers. The exposed files included highly sensitive data such as SSH keys, a password manager database, and personal media. This incident highlights severe privacy and security risks regarding AI assistants with deep access to local file systems.
Comments
0Discuss on Hacker NewsOnly full members can comment
Log in to express your opinion.
No comments yet.