news
558
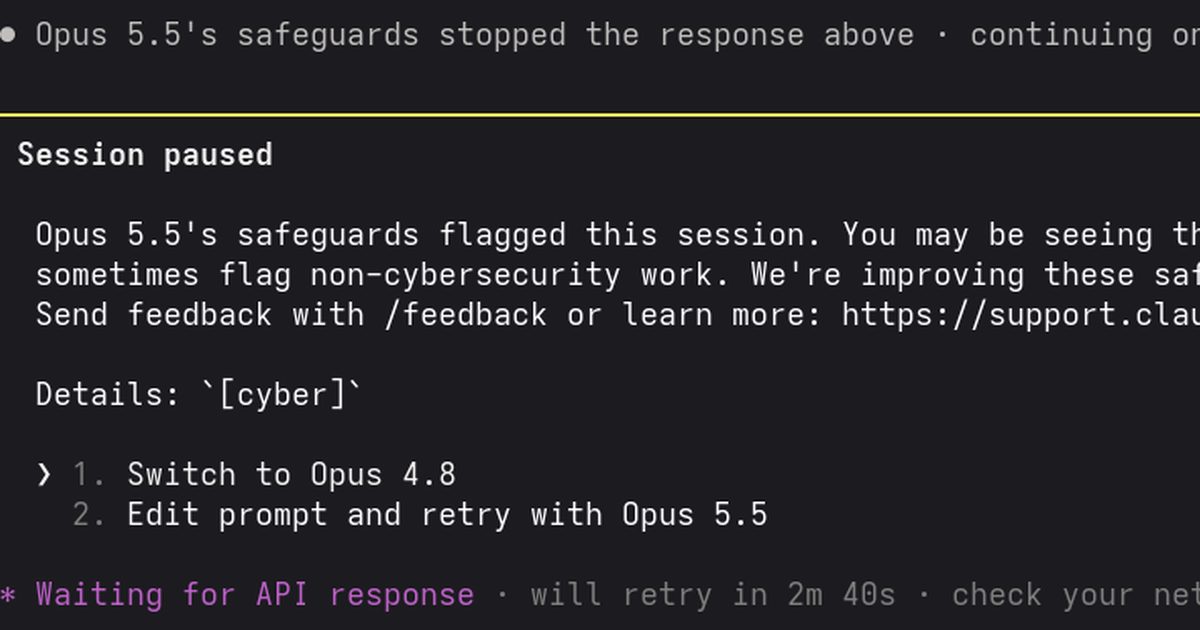
Fuck Your AI Safeguards
2026-11-19The article criticizes AI companies that acknowledge a reported security issue but decline to fix it, arguing that such safeguards are hollow. It contends that vendors should remediate disclosed vulnerabilities rather than dismiss them.
Comments
0Discuss on Hacker NewsOnly full members can comment
Log in to express your opinion.
No comments yet.