news
277
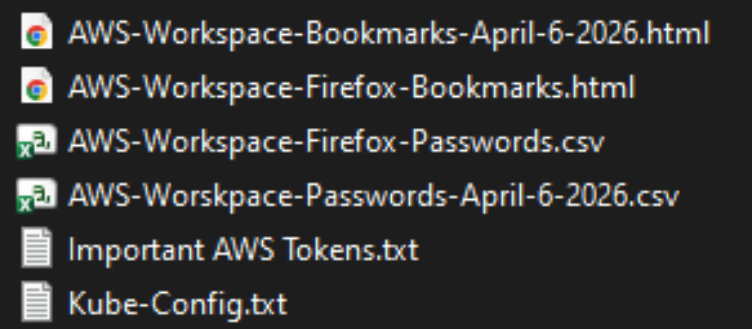
A CISA contractor exposed highly privileged AWS GovCloud credentials and access to numerous internal systems on a public GitHub repository. The sensitive keys remained publicly accessible until they were discovered and removed this past weekend. The incident has prompted security experts to raise concerns regarding the federal agency's operational security practices.
Comments
0Discuss on Hacker NewsOnly full members can comment
Log in to express your opinion.
No comments yet.