news
236
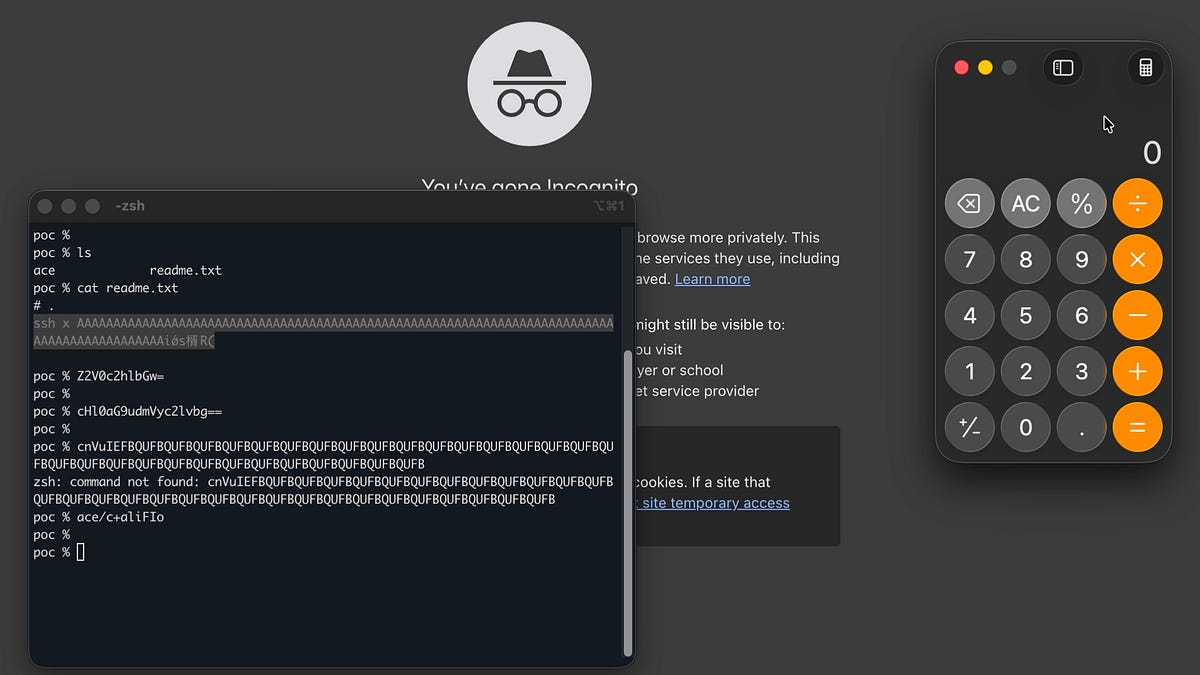
A newly identified vulnerability in the iTerm2 terminal emulator allows attackers to turn a simple "cat readme.txt" command into arbitrary code execution. By exploiting how the application processes terminal output, hackers can weaponize seemingly harmless file reads to run malicious scripts.
Comments
0Discuss on Hacker NewsOnly full members can comment
Log in to express your opinion.
No comments yet.