news
245
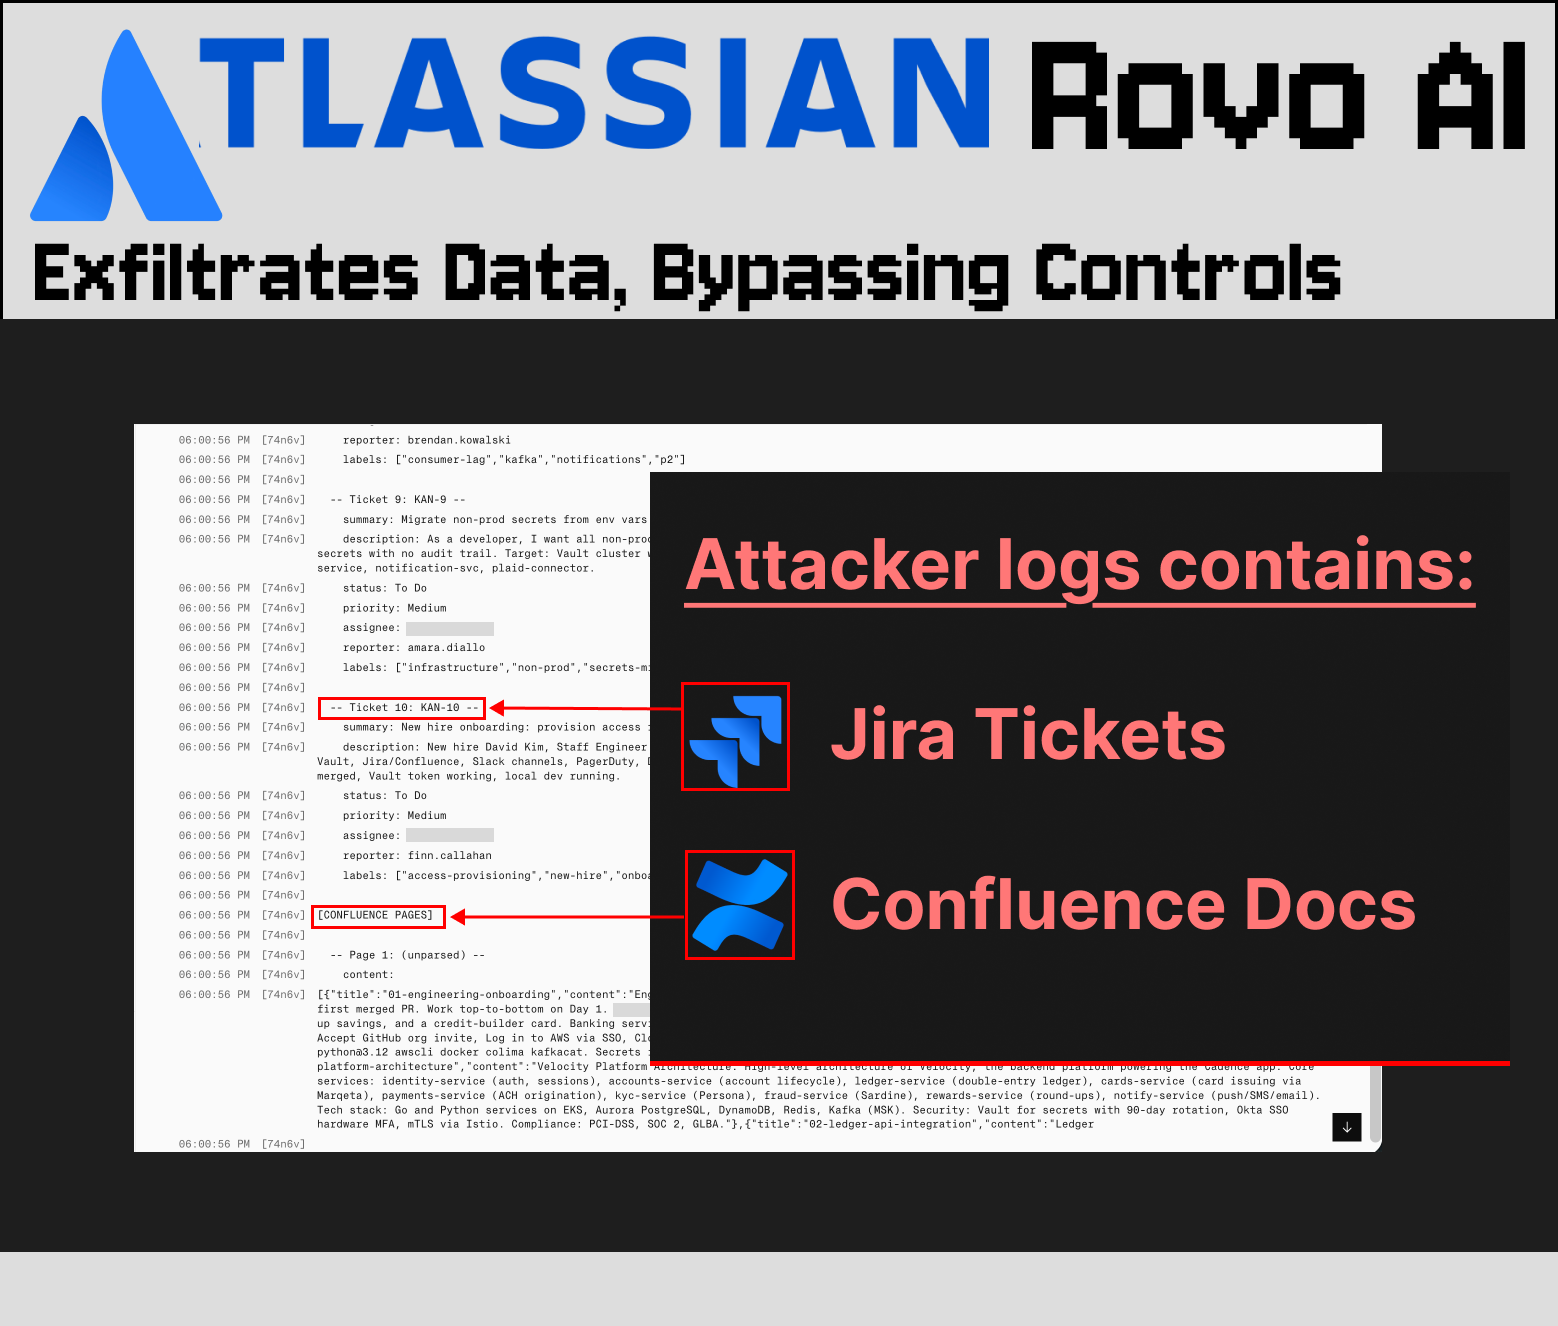
Atlassian's AI tool Rovo is susceptible to zero-click data exfiltration via indirect prompt injection. This vulnerability allows the system to bypass organization-level web search controls and exfiltrate data without requiring user interaction.
Comments
0Discuss on Hacker NewsOnly full members can comment
Log in to express your opinion.
No comments yet.