Tech TMA CIO News
This section is aimed at readers who follow enterprise technology leadership. It compiles news relevant to CIOs and IT decision-makers, including corporate technology strategy, cloud and software adoption, vendor moves, and management trends. The goal is a useful stream of stories about how large organizations run and modernize their technology.
Coverage typically features enterprise AI rollouts and their measured returns, cloud cost and repatriation debates, major vendor pricing and licensing changes, cybersecurity posture after high-profile breaches, and surveys of IT budget priorities. Leadership moves at large technology organizations also make the feed.
Enterprise technology decisions involve long contracts and organization-wide consequences, so leaders need signal rather than hype before committing. CIOs, IT directors, architects, and the consultants and vendors who serve them follow this coverage to benchmark their choices against what peers are actually doing.
A recent satirical tech commentary highlights the rampant supply chain vulnerabilities plaguing a major software package manager where malicious uploads are a frequent occurrence. Application security engineer Kevin Patel of NISC emphasizes the industry's resigned attitude toward these regular breaches, noting the frustrating lack of effective preventative measures. The piece serves as a sharp critique of the inadequate security oversight and automated publishing processes inherent in popular open-source ecosystems.
Comments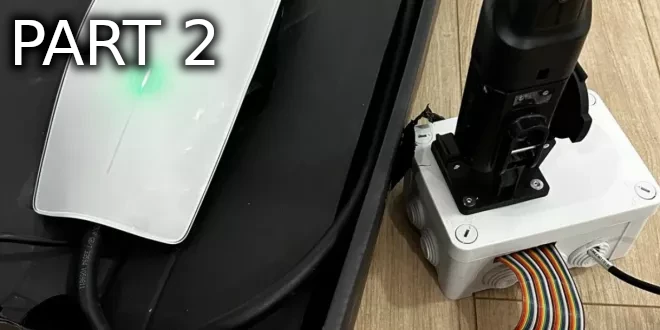
A newly discovered vulnerability in Tesla Wall Connectors allows attackers to bypass firmware downgrade protections by exploiting the bootloader through the physical charge port connector. This flaw could enable malicious actors to install older, potentially insecure firmware versions on the electric vehicle charging stations.
Comments
A sophisticated supply-chain attack compromised 42 TanStack packages on the npm registry after an attacker exploited GitHub Actions vulnerabilities to publish 84 malicious versions. The breach chained a pull request exploit with cache poisoning and OIDC token extraction, prompting developers to review the official postmortem and audit their dependencies.
Comments
A sophisticated cyber campaign is exploiting a malicious Obsidian note-taking app plugin to deploy a new remote access trojan named PHANTOMPULSE. The malware is specifically targeting victims operating within the finance and cryptocurrency sectors.
CommentsDebian must ship reproducible packages
2026-05-10Debian's push to mandate reproducible packages has sparked community debate over whether the achievement is worth the increased contribution burden. Supporters praise the move as a vital security measure to protect build infrastructure from malicious compromises, while skeptics argue it offers little defense against compromised upstream source dependencies. However, proponents point out that recent supply chain incidents like the xz utils backdoor demonstrate that securing the build pipeline itself remains essential.
Comments
Researchers at Baylor College of Medicine discovered that the human hippocampus remains capable of sophisticated language processing even when a patient is fully unconscious under anesthesia. This finding highlights the remarkable plasticity of the brain and suggests that the anesthetized mind retains complex cognitive functions previously thought to be lost.
CommentsRecent analysis of the XZ Utils backdoor suggests that the GNU IFUNC mechanism was the fundamental enabler of the exploit, transforming a standard supply chain compromise into a deeply hidden system-level threat. By weaponizing indirect function resolution, the attacker successfully concealed malicious code within the liblzma library, highlighting a critical need to reevaluate the security implications of IFUNC features in modern build systems.
CommentsThree Inverse Laws of AI
2026-05-05A recent article on the inverse laws of AI warns against anthropomorphizing artificial intelligence to prevent emotional dependence and flawed judgment. However, readers push back by arguing that humans naturally project empathy onto superficial cues, making an emotional attachment to advanced AI ultimately inevitable. The ensuing debate highlights the philosophical complexities of machine consciousness and the deep-seated cognitive biases humans use to relate to non-human entities.
Comments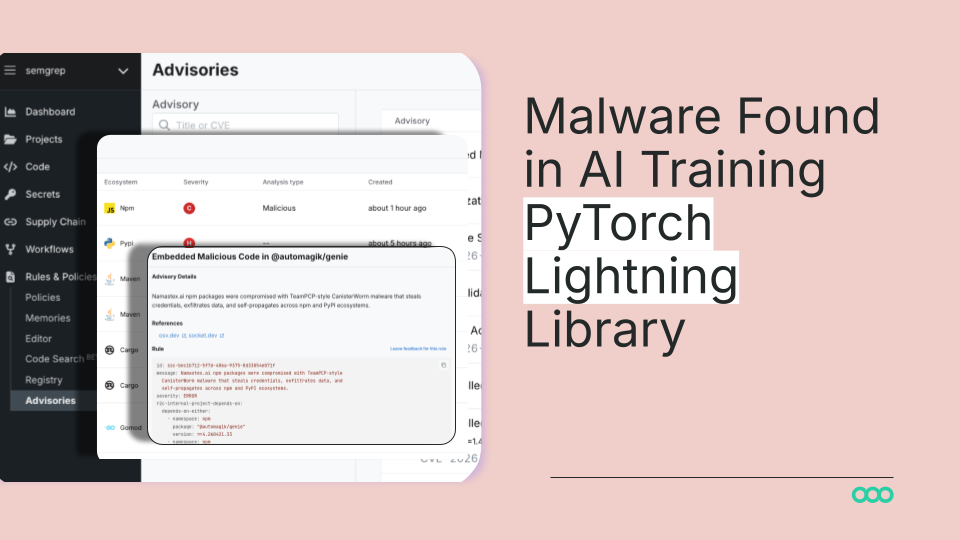
The PyPI package for the PyTorch Lightning AI training library was compromised in versions 2.6.2 and 2.6.3 with malicious code. The injected Mini Shai-Hulud themed payload executes credential-stealing malware whenever the library is imported by a user. Developers should avoid these specific versions to prevent unauthorized access to their sensitive data.
Comments
OpenAI and AWS have partnered to make OpenAI's models available on Amazon Bedrock, a move discussed by CEOs Sam Altman and Matt Garman in a new interview. The coverage also includes analysis on how this expansion relates to OpenAI's recent deal with Microsoft.
CommentsThe woes of sanitizing SVGs
2026-04-27The persistent security vulnerabilities associated with sanitizing SVGs can be effectively mitigated by implementing strict Content Security Policies. Developers can reliably secure untrusted content by combining iframe sandboxing with HTML meta tags to enforce permanent, restrictive CSP rules. Although currently underutilized due to poor documentation and minor UX friction, this sandboxing approach provides a highly robust defense against malicious scripts and phishing.
CommentsThe Onion to Take over InfoWars
2026-04-23Satirical news outlet The Onion has announced a mock acquisition of the conspiracy platform InfoWars for less than one trillion dollars. In a humorous press release, the publication pledged to expand the site's legacy of radicalization by transforming it into a digital hellscape of scams and malicious misinformation. The announcement also detailed plans to engineer a hypothetical meme so offensively potent that viewing it would cause readers to suffer fatal aneurysms.
Comments
A Brief History of Fish Sauce
2026-04-20This article explores the rich history of fish sauce, tracing its origins from ancient Asian recipes to its widespread use during the Roman Empire. It details how this pungent condiment evolved over the centuries to become a beloved staple in modern global cuisine, highlighting its many delicious contemporary uses.
CommentsThe author shares their initial experience configuring AMD's ROCm software stack on the new Strix Halo platform, highlighting the efficient sharing of 128GB unified memory between the CPU and GPU. The article also details their chosen operating system and walks through the driver installation process.
Comments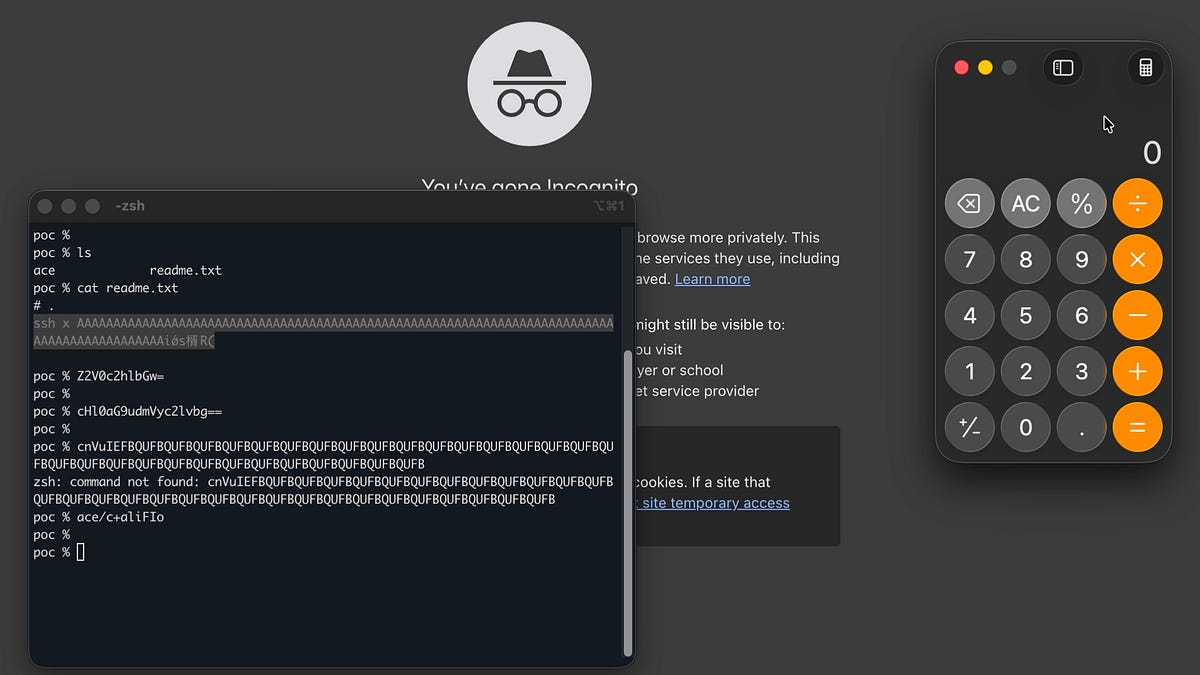
A newly identified vulnerability in the iTerm2 terminal emulator allows attackers to turn a simple "cat readme.txt" command into arbitrary code execution. By exploiting how the application processes terminal output, hackers can weaponize seemingly harmless file reads to run malicious scripts.
Comments
Ban the sale of precise geolocation
2026-04-17The latest edition of the Seriously Risky Business cybersecurity newsletter, now published on Lawfare, advocates for a strict ban on the commercial sale of precise geolocation data. The piece highlights the significant privacy and national security threats posed when data brokers sell highly accurate location tracking information to potentially malicious actors.
Comments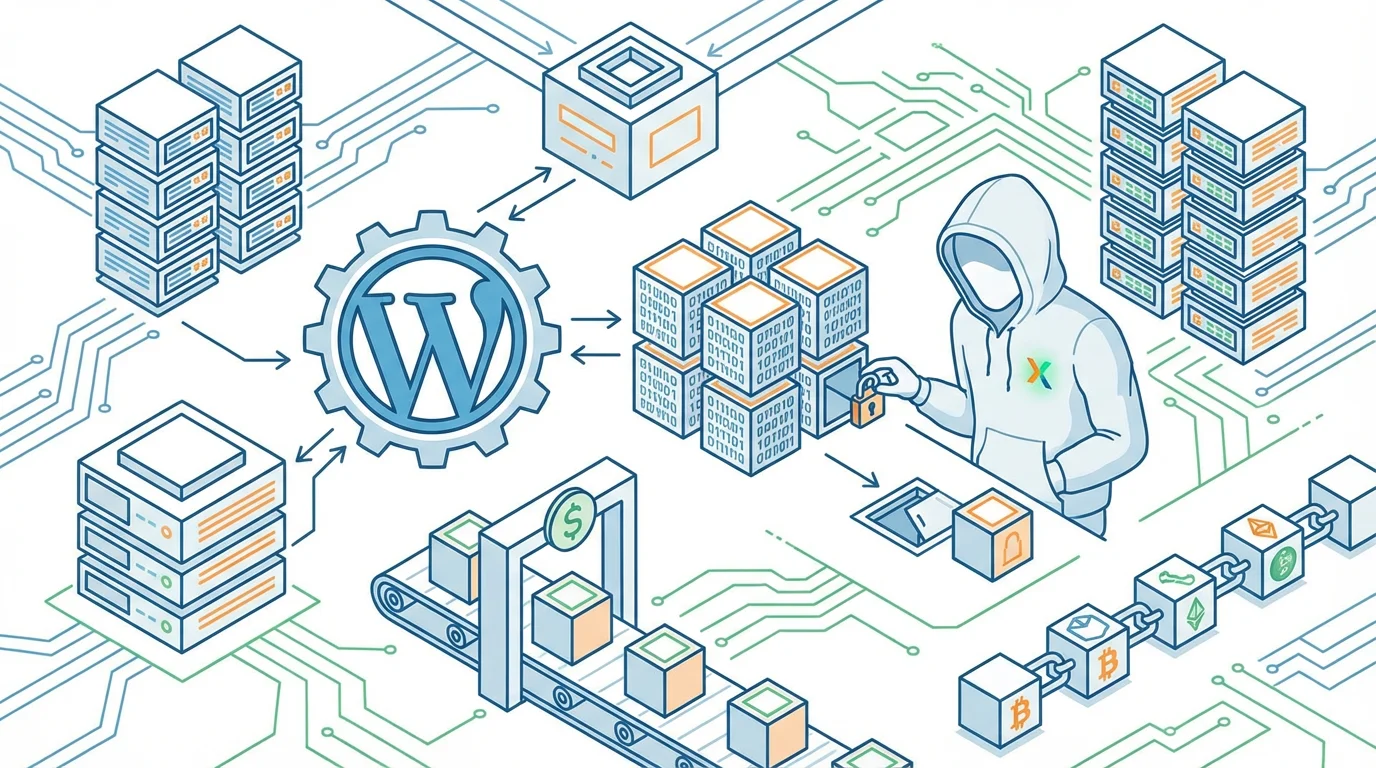
A malicious actor recently purchased 30 WordPress plugins and embedded backdoors into all of them, escalating a growing trend of supply chain attacks. This follows a similar incident involving the Widget Logic plugin, where a new owner compromised a trusted name to distribute malicious code. The coordinated compromise highlights the ongoing security risks associated with third-party plugin acquisitions in the WordPress ecosystem.
Comments
Spaghetti code doesn't just look bad, it makes code brittle and prone to bugs. A modular programming architecture decouples interdependency and makes your code more robust.
Comments
Git Flow vs. Trunk-based Development
2021-03-01Version control systems helped transform the way we execute and manage software projects. Should we use GitFlow or trunk-based development method? This guide lists the pros and cons of both, and looks at various use cases.
Comments
Shopping online is more popular than ever. Let's explore marketplace business models and payment methods for both regional and global services.
Comments