Hacker Breach News Today
Data breaches keep reshaping how companies think about security. Articles in this section cover newly disclosed intrusions, the techniques attackers used, the scale of exposed data, and how affected organizations respond, along with lessons defenders can draw from each incident.
Reports here span everything from ransomware crippling large enterprises to leaked credential databases, supply chain compromises, and quiet intrusions discovered months after the fact. Follow-up pieces examine regulatory penalties, class action fallout, and how honestly companies communicate with affected users.
Security teams read breach coverage the way pilots study accident reports, extracting patterns that prevent the next failure. For everyone else, these stories are a reminder of where personal data actually goes, and they often prompt practical steps like enabling stronger authentication.
GitHub confirmed a security breach affecting approximately 3,800 of its internal repositories. The compromise occurred after a company employee installed a malicious Visual Studio Code extension.
Comments
GitHub is investigating unauthorized access to its internal repositories. The company stated there is currently no evidence indicating that customer data or external repositories were compromised by the breach.
Comments
A recent satirical tech commentary highlights the rampant supply chain vulnerabilities plaguing a major software package manager where malicious uploads are a frequent occurrence. Application security engineer Kevin Patel of NISC emphasizes the industry's resigned attitude toward these regular breaches, noting the frustrating lack of effective preventative measures. The piece serves as a sharp critique of the inadequate security oversight and automated publishing processes inherent in popular open-source ecosystems.
Comments
Education technology company Instructure paid a ransom to hackers after its Canvas learning management system was breached twice. In exchange, the cybercriminals returned the compromised personal data of 275 million users across more than 8,800 institutions. Instructure assured its users that no customers will face further extortion from this incident.
Comments
A sophisticated supply-chain attack compromised 42 TanStack packages on the npm registry after an attacker exploited GitHub Actions vulnerabilities to publish 84 malicious versions. The breach chained a pull request exploit with cache poisoning and OIDC token extraction, prompting developers to review the official postmortem and audit their dependencies.
Comments
Instructure's Canvas learning management platform has been restored online following a disruption caused by a confirmed data breach. The ShinyHunters hacking group claimed responsibility for the incident and is threatening to leak sensitive school data if ransom demands are not met.
Comments
Dunwoody, Georgia residents are furious after learning that surveillance firm Flock accessed cameras inside a children's gymnastics room during a sales demonstration. The privacy breach has sparked intense backlash against the city's surveillance contract, prompting citizens to question whether local elected officials actually care about the incident.
Comments
Mercor, a company specializing in AI voice authenticity and deepfake detection, has suffered a data breach resulting in the theft of 4TB of voice samples. The compromised audio data belongs to 40,000 AI contractors whose recordings are used to train and verify the firm's audio forensics infrastructure.
Comments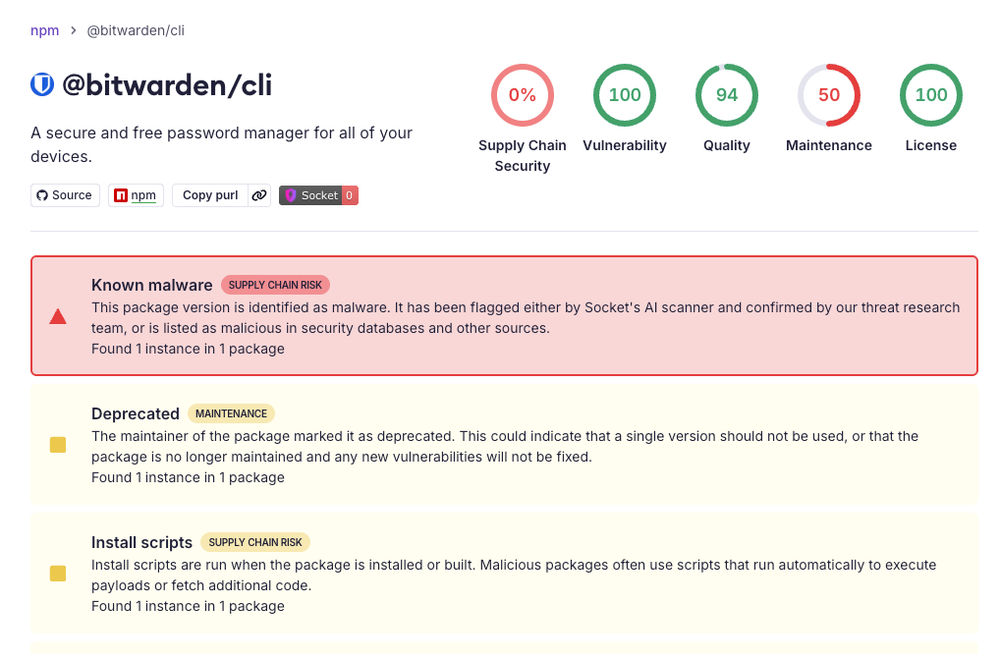
Bitwarden CLI version 2026.4.0 was compromised after attackers abused a GitHub Action within Bitwarden's CI/CD pipeline. This breach is part of the ongoing Checkmarx supply chain campaign.
Comments
France Titres, the French government agency responsible for issuing administrative documents, has confirmed a data breach involving stolen citizen data. The disclosure follows claims from a threat actor who compromised the system and is now offering the stolen information for sale.
Comments
A recent OAuth supply chain compromise at Vercel highlights how trusted third-party applications and platform environment variables can bypass traditional defenses to significantly amplify a breach's impact. This incident underscores the critical need for developers to reassess software supply chain risks and the underlying design tradeoffs of modern PaaS environments.
Comments
Vercel suffered a significant data breach after an employee at the AI startup Context AI inadvertently installed malware from a Roblox cheat, enabling attackers to exploit an OAuth integration and access internal systems. The incident led to the exfiltration of non-sensitive environment variables and has forced thousands of developers to undertake massive credential rotation efforts. Ultimately, the attack underscores the severe security vulnerabilities introduced by granting broad access permissions to third-party AI productivity tools.
Comments
The European Commission recently launched a new age verification app, claiming the technology was fully prepared for deployment, but cybersecurity experts quickly identified critical flaws. Hackers successfully breached the application in just two minutes, exposing significant security vulnerabilities in the EU digital initiative.
Comments
Vercel April 2026 security incident
2026-04-19Cloud development platform Vercel has disclosed a security incident after threat actors claimed to have breached its systems. The attackers are currently attempting to sell the stolen data.
Comments
Vercel disclosed a security breach impacting its internal systems that came to light on Sunday. The company has brought in an incident response provider to investigate the intrusion, though specific details regarding the scope of the attack remain scarce.
Comments
This year’s insane timeline of hacks
2026-04-13A newly compiled archive details a staggering timeline of major cybersecurity breaches that have largely flown under the radar this year. By documenting these underreported hacks, the collection sheds light on the escalating and often overlooked digital threats facing modern organizations.
Comments